Fandango Checkout Breach Exposed 69,665 Payment Cards.
Fandango reported an October 8-11 checkout breach exposed card numbers, CVVs, and emails for 69,665 people.
Peach disclosed Yumirulink's Cuenote FC breach exposed 8.99M records including names, addresses, and itineraries.
Peach Aviation disclosed on 20 November 2026 that unauthorized access to Yumirulink's Cuenote FC email service exposed 8,997,106 customer records including names, birth dates, gender, addresses, phone numbers, email addresses, and itinerary details. Credit-card and passport data were not involved. The intrusion occurred on 18 October; Yumirulink shut down all Cuenote FC functions, and affected services remain suspended.
Peach Aviation, a low-cost carrier under ANA Holdings, disclosed on 20 November 2026 that 8,997,106 customer records were exposed following unauthorized access to Yumirulink's Cuenote FC email-delivery service. According to Peach's English-language notice (PDF), the intrusion occurred on 18 October 2026 at Yumirulink's server environment. Exposed information includes names, dates of birth, gender, addresses, phone numbers, email addresses, and itinerary details. Credit-card and passport information was not involved, and the airline says reservations, reservation changes, and flight operations are unaffected.
High High because nearly 9 million records with full names, contact details, and real travel itineraries can fuel highly targeted phishing campaigns that reference specific flights or booking dates to appear legitimate.
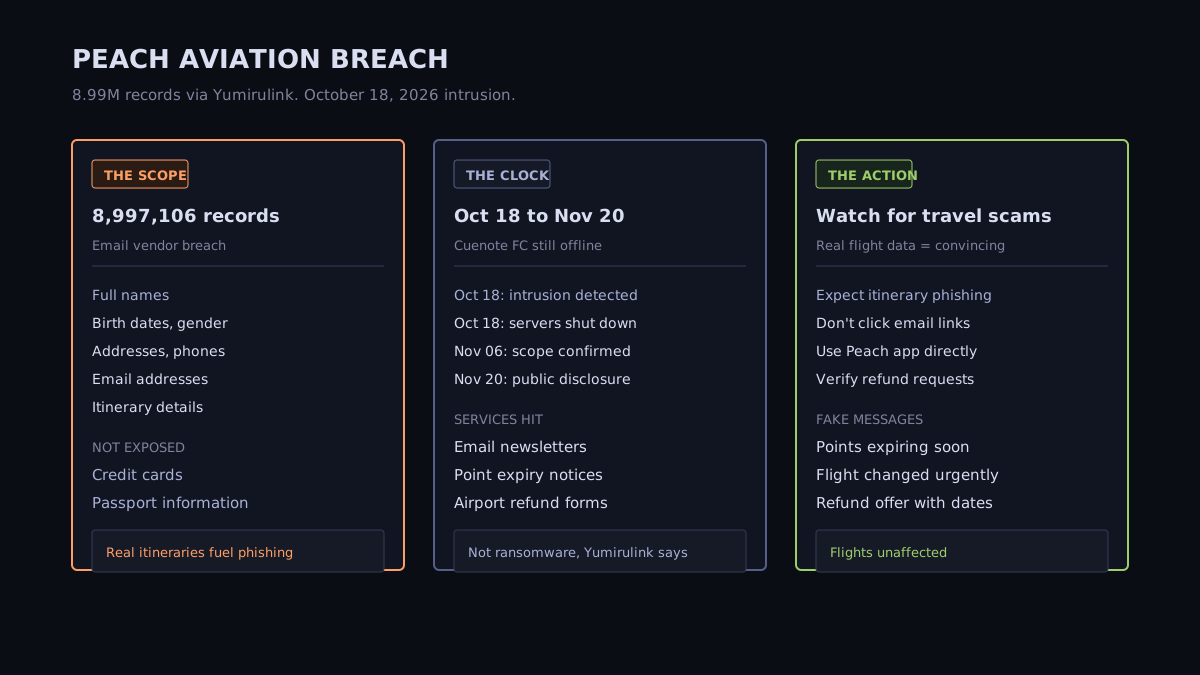
Peach Aviation uses Cuenote FC, an email-delivery service provided by Yumirulink Inc., to send newsletters, automated notifications such as Peach Point expiration reminders, and to host an airport refund application form used during irregular operations like flight cancellations or delays. On 18 October 2026, Yumirulink detected unauthorized third-party access to certain servers in the Cuenote FC environment and shut down the server OS and suspended all functions as an emergency measure, according to Peach's Japanese-language notice (PDF).
| Event | Date |
|---|---|
| Unauthorized access detected at Yumirulink | 2026-10-18 (Sunday) |
| Yumirulink shuts down servers, suspends all Cuenote FC functions | 2026-10-18 |
| Yumirulink confirms scope of impacted services to Peach | 2026-11-06 (Friday) |
| Peach determines customer information was exposed | 2026-11-20 |
| Peach begins notifying affected customers by email | 2026-11-20 |
Nikkei reports that Yumirulink notified Peach of the unauthorized access on 19 October, and on 6 November confirmed which services were affected. Peach then investigated to determine the final scope and publicly disclosed the breach on 20 November after completing its analysis. Yumirulink confirmed that the incident was not caused by ransomware but is still investigating the intrusion route and detailed impact, Peach's notice states.
Peach confirmed that 8,997,106 records were affected. IPCRIME notes that this figure counts records and should not be relabeled as a confirmed number of unique individuals without further explanation from the company, since one person could appear in multiple records if they subscribed to newsletters and also used the refund form.
According to Peach's notice, the following customer information may have been exposed:
Credit-card information and passport details are not included in the exposed data under any circumstances, Peach emphasizes. The airline has reported the incident to Japan's Personal Information Protection Commission (PPC) and says no secondary damage or unauthorized use of the personal information has been confirmed as of its statement.
The three services that remain suspended while Cuenote FC is offline are:
Nikkei explains that the refund form was built on Cuenote FC's infrastructure, so customers who submitted refund requests during irregular operations also had their information stored in the compromised system. Peach says it is handling refund requests through alternative procedures while the form remains unavailable.
flypeach.com directly into your browser instead.Peach is notifying affected customers sequentially by email to their registered addresses and has set up a general customer-service line at +852 2968 2222 (Monday to Friday, 9:00 to 17:30 Hong Kong time, excluding public holidays and typhoon or black rainstorm warnings), though this is the airline's standard support number, not a dedicated incident hotline. The airline has not disclosed when Cuenote FC services will resume or whether Yumirulink has identified the root cause.
No. The breach affected Yumirulink's email-delivery system, not Peach's reservation or flight-operations systems. Customers can still make and change reservations, and flights are operating normally.
Peach used Cuenote FC not only for newsletters and automated emails but also for an airport refund application form used during irregular operations such as flight disruptions. Customers who filled out that form at airports had their information stored in Cuenote FC.
No. Yumirulink confirmed the incident was not caused by ransomware. The company is investigating the intrusion route and detailed scope but has not disclosed the attack method.
Fandango reported an October 8-11 checkout breach exposed card numbers, CVVs, and emails for 69,665 people.
Plaid confirmed a 13 November intrusion into KARTE exposed 570 clients including MUFG, SMBC, ZOZO, Suntory, and J.League.
RIKEN disclosed a Fugaku intrusion exfiltrated 430 credentials including 233 SSH keys without passphrases.