Fandango Checkout Breach Exposed 69,665 Payment Cards.
Fandango reported an October 8-11 checkout breach exposed card numbers, CVVs, and emails for 69,665 people.
Extortion group n0n listed Samsung, Starbucks, Gap, Timberland and others on its leak site on 14 November 2026. These are claims, not confirmed breaches.
On 14 November 2026, extortion group n0n listed about 10 companies on its leak site, including Samsung, Starbucks, Timberland, Gap, VF Corporation, Alo Yoga, Airport Appliance and Steeden Financial. These are unverified claims. None of the named companies has confirmed a breach, and the size and authenticity of the claimed data are unknown.
Extortion group n0n named about 10 companies on its leak site on 14 November 2026. Threat trackers Brandefense ATLAS and HackerFeeds list Samsung Electronics, Starbucks, Timberland, Gap Inc., VF Corporation, Alo Yoga, Airport Appliance, Inc., Steeden Financial, Pollstar and MM Insurance Agency. These are claims made by the group. None of the companies has confirmed a breach, and nothing public yet shows that the claimed data is real or how much of it exists.
Medium Medium because nothing is confirmed, but public claims naming big consumer brands reliably feed brand-themed phishing against customers and staff.
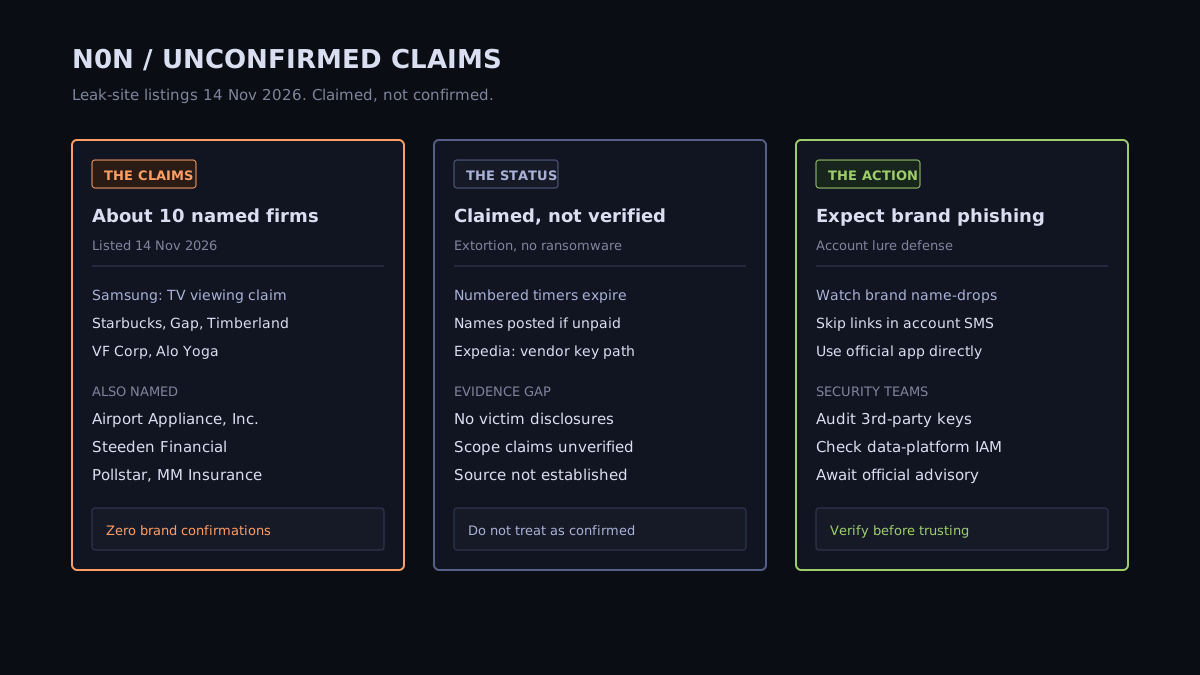
For Samsung, the H4ckmanac alert says n0n claims US Smart TV viewing records, household-level geographic information, advertising data and internal governance documents. The alert gives no data volume and marks the status as pending verification. Brandefense quotes a Timberland entry that claims storefront search and customer email data. Most other entries carry no description of what was taken.
We are not repeating any data from the listings. Until a named company confirms an incident, neither the authenticity nor the scope of the claimed files is established.
SecurityAffairs reported on 14 November that n0n claims to have taken nearly 1 billion Expedia traveler records. Expedia confirmed that attackers reached its systems through a compromised third-party data platform provider in a supply chain attack that also hit other companies. Expedia has not confirmed n0n's figures. Wiz and Sentra say the attackers used a stolen vendor key from Qubole, a Google Cloud partner.
Citing SOCRadar, SecurityAffairs describes n0n as a data theft and extortion group active since mid-September that does not use ransomware. Victims appear first as numbered companies with a countdown timer, and the group names a company only if it does not pay. That history is why defenders watch n0n closely. It does not make any single new listing true.
Until a named company confirms an incident, keep two lists apart: unverified extortion claims and confirmed breach disclosures.
No. As of 15 November 2026, none of the companies n0n named on 14 November has confirmed an intrusion or data theft. A leak-site post is an extortion claim until the organization or an independent investigation verifies it.
According to the H4ckmanac threat alert, n0n claims US Smart TV viewing records, household-level geographic information, device advertising features, advertising model training data and internal data governance documents. The alert lists the status as pending verification, and Samsung has not confirmed the claim.
SecurityAffairs, citing SOCRadar, reports that n0n emerged in mid-September 2026 and focuses on data theft and extortion without ransomware. Victims first appear as numbered companies with a countdown timer, and the group names a company only if it does not pay.
Fandango reported an October 8-11 checkout breach exposed card numbers, CVVs, and emails for 69,665 people.
Peach disclosed Yumirulink's Cuenote FC breach exposed 8.99M records including names, addresses, and itineraries.
Plaid confirmed a 13 November intrusion into KARTE exposed 570 clients including MUFG, SMBC, ZOZO, Suntory, and J.League.