v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
JFrog published CVE-2026-120338 on 1 November. The prefab-ui 0.21.0 wheel had been on PyPI since 26 October. GitHub's copy names no package.
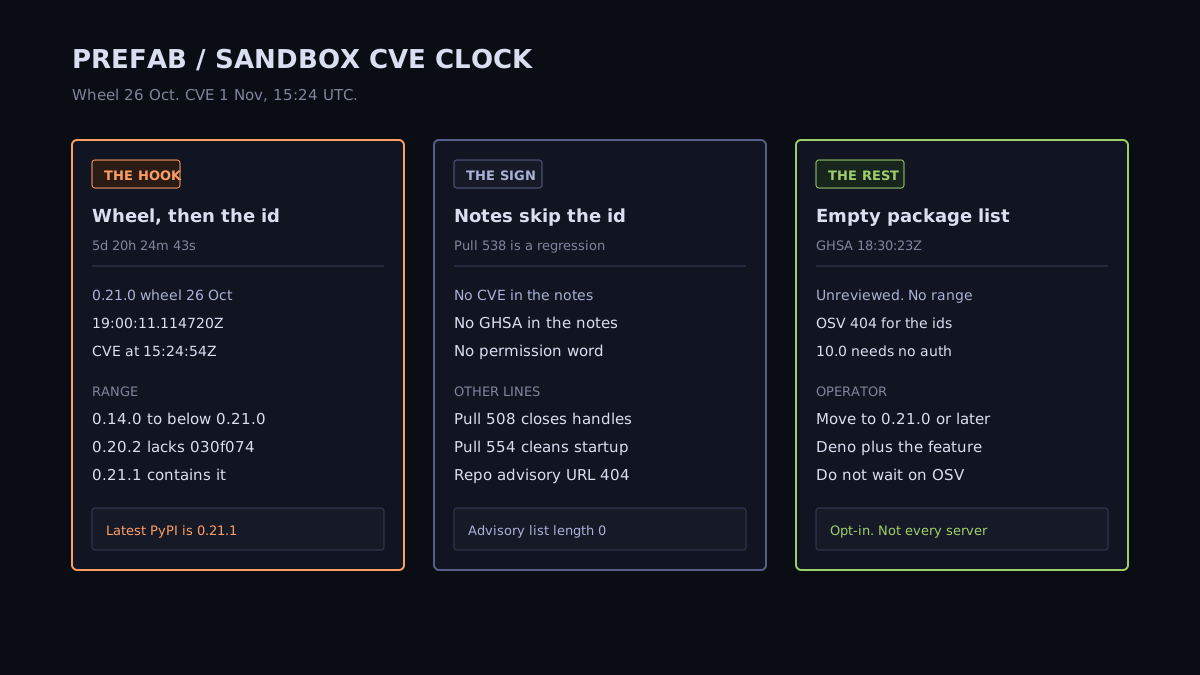
JFrog published CVE-2026-120338 at 15:24 UTC on 1 November. The prefab-ui 0.21.0 wheel had already been on PyPI for 5 days, 20 hours, and 24 minutes. Through 0.20.2 the Deno process that should isolate model-written UI keeps read, write, and network permission. GitHub's advisory is unreviewed and names no package range. OSV returned 404.
JFrog published CVE-2026-120338 at 15:24 UTC on 1 November. The prefab-ui 0.21.0 wheel that the record names as the fix had already been on PyPI since 26 October. The Hacker News front page this evening did not carry it. US trends at 22:24 UTC were NFL games and election names. x.com news returned 403.
Critical A documented sandbox for model-written UI. Critical because the CVE's unauthenticated scenario is CVSS 3.1 10.0. The same record scores an authenticated tool caller at 9.9. Generative UI is opt-in, and Deno has to be installed.
The primary is the CVE record. Assigner short name JFROG. State PUBLISHED. dateReserved 2026-11-01T15:12:50.987Z. datePublished and dateUpdated 2026-11-01T15:24:54.158Z. datePublic is absent. Reserve to publish is 12m 3.171s. No ADP container. CWE-94 is on the GitHub copy, not repeated as a separate CWE block here.
The affected range is prefab-ui 0.14.0 lessThan 0.21.0, versionType semver, defaultStatus unaffected. The files named are src/prefab_ui/sandbox/_pyodide.py and src/prefab_ui/sandbox/runner.js. This read did not open those files. The behavior below is the record.
| Mark | Clock |
|---|---|
| v0.14.0 GitHub release | 2026-03-27T02:35:48Z |
| 0.14.0 wheel | 2026-03-27T02:36:03.860380Z. 15.860s later |
| v0.20.2 GitHub release | 2026-06-03T02:13:25Z |
| 0.20.2 wheel | 2026-06-03T02:13:47.539028Z. 22.539s later |
| Pull 538 opened | 2026-10-25T18:30:37Z. Author login jlowin |
| Pull 538 merged | 2026-10-25T18:48:52Z. 18m 15s open |
| Commit 030f074 | Same second. Committer GitHub. Verified |
| v0.21.0 GitHub release | 2026-10-26T18:59:55Z. 1d 0h 11m 3s after the merge |
| 0.21.0 wheel | 2026-10-26T19:00:11.114720Z. 16.115s after the release |
| 0.21.1 wheel | 2026-10-26T19:18:06.375380Z. 17m 55.261s after 0.21.0 |
| CVE published | 2026-11-01T15:24:54.158Z. 5d 20h 24m 43.043s after the 0.21.0 wheel |
| NVD stamp on the GHSA | 2026-11-01T16:18:14Z. 53m 19.842s after the CVE |
| GHSA-3g72-rrqc-f76c | 2026-11-01T18:30:23Z. 3h 5m 28.842s after the CVE |
From the 0.14.0 wheel to the CVE is 219d 12h 48m 50.298s. From the 0.20.2 wheel to the 0.21.0 wheel is 145d 16h 46m 23.576s. None of those files is yanked. PyPI info.version tonight is 0.21.1. There is no 0.21.2 key.
Compare v0.20.2 to 030f074 is ahead, ahead 15, behind 0. The tag does not contain the commit. Compare v0.21.0 to the commit is behind, ahead 0, behind 20. Compare the commit to v0.21.1 is ahead, ahead 21, behind 0. Both fixed tags contain it. v0.14.0 compared to the commit is ahead, ahead 93, behind 0.
The release title is "v0.21.0: UI, Robot." The lead paragraph is AppTool, so a Prefab app can expose tools to its MCP host. It says host support for app-provided tools is still limited. That feature is not this CVE.
The runtime bullet says "sandbox lifecycle and output handling fixes." The changelog then lists three different sandbox lines. Pull 508 is "Close Deno sandbox subprocess handles." Pull 538 is the regression line above. Pull 554 is "Clean up cancelled sandbox startup." The CVE names pull 538 and commit 030f074. It does not name 508 or 554. This read did not diff 508 or 554. Do not treat every sandbox word in the notes as the permission fix.
The record says that through 0.20.2 the sandbox starts Deno with read, write, and network permission, and leaves the Deno API where the Python in the sandbox can call it. A caller who can supply that code can read and write as the server OS user, and a write can persist in the server environment. The usual remote path it names is FastMCP's GenerativeUI provider, which forwards a tool argument into this sandbox. On a server with no authentication, any client who can reach it can call the tool. With authentication, any client allowed to call tools can. The fix text says 0.21.0 revokes those permissions after startup, starts the process so a later prompt cannot grant them again, and limits bootstrap network to cdn.jsdelivr.net.
The CVE links a repository advisory, GHSA-595q-jv4r-q7j9. The unauthenticated API for that advisory returns 404. The HTML URL returns 404. The repository security-advisory list length is 0. PrefectHQ/prefab pushed_at is 2026-10-26T19:18:11Z, which is the 0.21.1 window, not a 1 November advisory publish.
GHSA-3g72-rrqc-f76c was published at 2026-11-01T18:30:23Z and updated at 2026-11-01T18:30:24Z. Severity critical. The CVSS 3.1 vector matches the CVE's 10.0 score: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H. The CVSS 4.0 vector on that record is null and the score is 0.0. github_reviewed_at is null. type is unreviewed. vulnerabilities is an empty array. Credits is empty. nvd_published_at is 2026-11-01T16:18:14Z, which is before the GHSA publish. From that NVD stamp to the GHSA is 2h 12m 9s.
OSV returned 404 for CVE-2026-120338, for GHSA-3g72-rrqc-f76c, and for GHSA-595q-jv4r-q7j9. A scanner that only reads OSV, or only reads a reviewed GitHub package range, does not learn 0.20.2 from those endpoints on this read. The floor is the CVE's lessThan 0.21.0.
The CVE prints two scenarios, not one score for every install. The 10.0 scenario is a FastMCP server with GenerativeUI enabled, Deno installed, and no authentication configured. The 9.9 scenario is an authenticated client allowed to call tools, vector CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H. The GitHub advisory text repeats the 10.0 description and says the finding was confirmed on prefab-ui 0.20.2. It does not add a third score.
If the process has Deno and registers Generative UI, move prefab-ui to 0.21.0 or later. PyPI latest tonight is 0.21.1, and that tag contains 030f074. 0.21.1 does not claim a second sandbox fix. Pin either fixed release. Do not wait for an OSV id before you move a server that matches the 10.0 scenario.
Until that upgrade, do not register Generative UI on a host untrusted clients can reach. The record's condition is the feature plus Deno. A Prefab install that never starts that sandbox is outside the affected text.
Read the 0.21.0 notes as a product release. Then read the CVE for the permission change. The changelog line for pull 538 will not tell you which sandbox sentence is the one that matters.
No. GitHub v0.21.1 was published at 2026-10-26T19:17:48Z. The note is a docs preview mount after a Vite upgrade, pull 556, one commit ahead of v0.21.0. The CVE range stops below 0.21.0. Compare says both tags contain commit 030f074.
Not from the ids checked on this read. OSV returned 404 for CVE-2026-120338, GHSA-3g72-rrqc-f76c, and GHSA-595q-jv4r-q7j9. The GitHub advisory is unreviewed, github_reviewed_at is empty, and the vulnerabilities array is empty. The floor is in the CVE text.
No. The 10.0 scenario is a FastMCP server with Generative UI enabled, Deno installed, and no authentication. The 9.9 scenario is an authenticated client allowed to call tools on a server that runs untrusted code in that sandbox. A server that never starts it is outside the record.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.