v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.
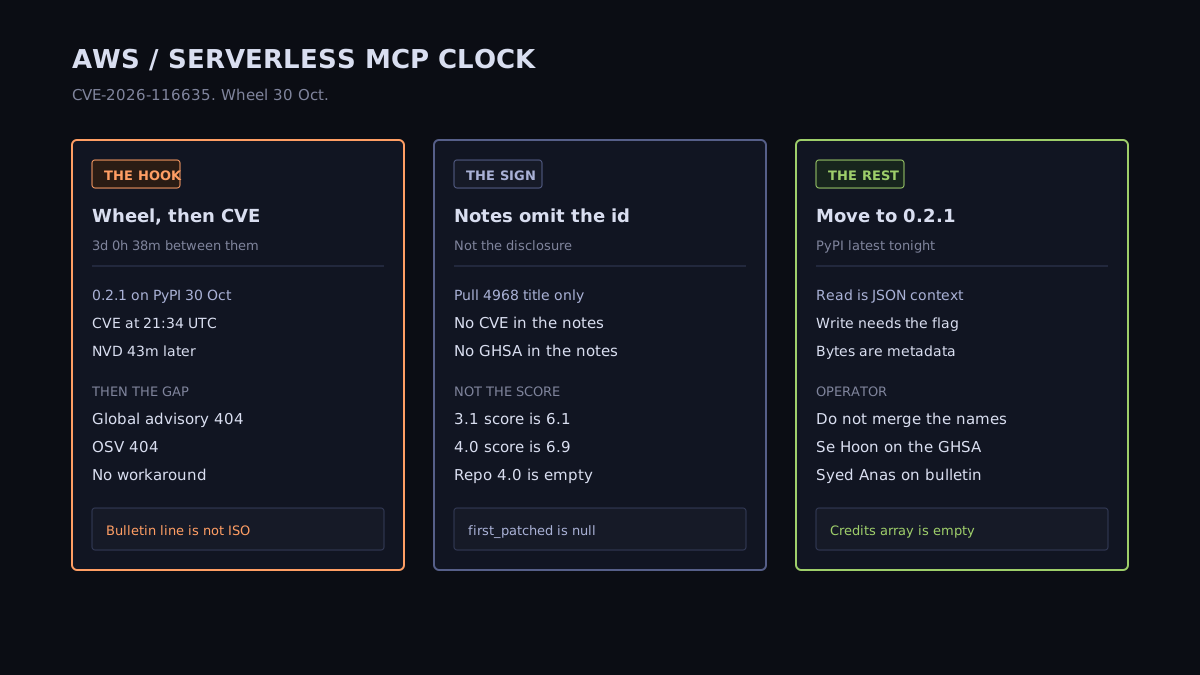
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The awslabs.aws-serverless-mcp-server 0.2.1 wheel had already been on PyPI for 3 days and 38 minutes. Below 0.2.1 a project name can send a deployment-status read to a JSON file outside that directory. Writing needs the enable-write flag. The global advisory API and OSV both return 404.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The awslabs.aws-serverless-mcp-server 0.2.1 wheel that the record names as the fix had already been on PyPI since 30 October. The Hacker News front page this evening did not carry it. US trends at 22:36 UTC were an election slate and Monday Night Football. x.com news returned 403.
Medium A project name on the deployment-status path. Medium because the scored 3.1 vector is 6.1 and local. The same CVE also prints a 4.0 score of 6.9. The bulletin's content type says Important. That word is not a third score.
The primary is the CVE record. Assigner short name AMZN. State PUBLISHED. dateReserved 2026-10-26T18:00:54.383Z. datePublished and dateUpdated 2026-11-02T21:34:09.483Z. datePublic is absent. Reserve to publish is 7d 3h 33m 15.100s. No ADP container. CWE-23 and CWE-36 are on the record. The affected range is version 0 lessThan 0.2.1, versionType custom, defaultStatus unaffected.
The behavior below is the record and the repo advisory. This read did not open the patched files.
| Mark | Clock |
|---|---|
| CVE reserved | 2026-10-26T18:00:54.383Z |
| PyPI 0.2.0 wheel | 2026-08-26T19:33:42.238901Z. Not yanked |
| Pull 4968 merged | 2026-10-30T20:03:11Z. Author login reedham-aws |
| Commit 2d00caf | Committer 2026-10-30T20:02:20Z. Verified. pyproject still says 0.2.0 |
| Release commit bc03aaf | 2026-10-30T20:33:33Z. pyproject says 0.2.1 |
| 0.2.1 wheel | 2026-10-30T20:56:05.482440Z. 22m 32.482s after bc03aaf |
| GitHub release published | 2026-10-30T21:18:01Z. 21m 55.518s after the wheel |
| CVE published | 2026-11-02T21:34:09.483Z. 3d 0h 38m 4.001s after the wheel |
| Repo GHSA | 2026-11-02T21:34:49Z. 39.517s after the CVE |
| NVD published | 2026-11-02T22:17:19.130Z. 43m 9.647s after the CVE |
From the 0.2.0 wheel to the 0.2.1 wheel is 65d 1h 22m 23.244s. None of the 23 release keys is yanked. PyPI info.version tonight is 0.2.1. There is no 0.2.2 key.
Compare the 27 October tag commit 1bf810fd to 2d00caf is behind, ahead 0, behind 81. That tag's pyproject says 0.2.0 and does not contain the merge. Compare 2d00caf to bc03aaf is ahead, ahead 1, behind 0. The release commit contains the merge, and its pyproject says 0.2.1. The merge commit itself still says 0.2.0. The version operators install is the bump, not the validation commit alone.
GHSA-r6mm-377j-qg8m was published at 2026-11-02T21:34:49Z and updated at 2026-11-02T21:34:50Z. Severity medium. The CVSS 3.1 vector matches the CVE's 6.1 score: CVSS:3.1/AV:L/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:N. The CVSS 4.0 vector on that advisory is null. Credits is an empty array. The range string is <0.2.1. first_patched_version is null. The unauthenticated global API for this GHSA returns 404.
The CVE's second score is 4.0, base 6.9, vector CVSS:4.0/AV:L/AC:L/AT:N/PR:N/UI:P/VC:H/VI:L/VA:N/SC:N/SI:N/SA:N. Do not paste that 6.9 onto the repo advisory. The advisory did not print it.
OSV returned 404 for CVE-2026-116635 and for GHSA-r6mm-377j-qg8m. A scanner that only reads OSV, or only reads a reviewed GitHub package range, does not learn 0.2.0 from those endpoints on this read. The floor is the CVE's lessThan 0.2.1.
The record says an actor who can influence the MCP agent may read a JSON file outside the deployment-status directory, and, where write access has been enabled, may create or overwrite a JSON file outside that directory. The repo advisory says the read returns that file into the agent context, and the write clobbers a file with deployment metadata. The path it names is the project name. There is no workaround sentence on the advisory or on bulletin 2026-164-AWS.
The bulletin prints Publication Date: 11/02/2026 13:30 PM PST. That string is not an ISO timestamp. Do not treat it as a second measured minute beside 21:34:09.483Z.
The repo advisory prose says it thanks Se Hoon (bebold6133). The bulletin prose says it thanks Syed Anas Mohiuddin. Both sentences end with the coordinated disclosure line. The credits array on the advisory is empty. This read did not find a page that says the two strings are one person, and it did not find a page that says they are two. Quote the line you opened.
Pull 4968's file list includes deployment_manager.py, deploy_webapp.py, models.py, and server.py under the serverless package, plus tests. This read did not open those files and did not print a path.
If the installed package is below 0.2.1, move to 0.2.1. PyPI latest tonight is that version. The advisory and the bulletin both say there is no workaround. A fork has to take the same validation change. The release note will not tell you that.
Until that upgrade, treat a project name that you did not set as a read of JSON outside the deployment-status directory. Turn the enable-write flag off unless you mean a deployment-metadata write to land on that path. The record does not name a credential to rotate. If a JSON file outside that directory held a secret, treat the file as exposed. Do not invent a broader theft from a score of 6.1.
The 30 October wheel is the package clock. The 2 November CVE is the impact clock. They are 3 days and 38 minutes apart, and the note in between does not say CVE.
The 3.1 vector is local, low complexity, no privileges, user interaction required, scope unchanged. Confidentiality is high, integrity low, availability none. The text says an actor who can influence the MCP agent. That is the interaction. It is not an unauthenticated scan of a listening port, and it is not a claim that a project name in a tool call is harmless.
The advisory separates them. A read returns a JSON file from outside the deployment-status directory into the agent context. A write is described only where write access has been enabled, and the bytes written are deployment metadata, which can clobber an existing file. The bulletin says there is no workaround. The fix version is 0.2.1.
The repo advisory prose thanks Se Hoon (bebold6133). The AWS bulletin prose thanks Syed Anas Mohiuddin. The advisory credits array is empty. This read did not find a third page that maps one string to the other.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Reviewed GHSA-j656-3hf2-fvjc went up at 17:57 UTC on 2 November with an empty CVE field. npm 0.22.6 has been the fixed build since 24 June.