v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
Reviewed GHSA-j656-3hf2-fvjc went up at 17:57 UTC on 2 November with an empty CVE field. npm 0.22.6 has been the fixed build since 24 June.
GitHub published reviewed advisory GHSA-j656-3hf2-fvjc at 17:57 UTC on 2 November and left the CVE field empty. The npm package it marks fixed, @bytebase/dbhub 0.22.6, has been up since 24 June. CVE-2026-61789 was published on 30 October. The repo copy says high and stores no CVSS vector. The reviewed score is CVSS 4.0 6.1. Latest tonight is 1.5.0.
GitHub published reviewed advisory GHSA-j656-3hf2-fvjc at 17:57 UTC on 2 November. The @bytebase/dbhub 0.22.6 package that record marks as the fix has been on npm since 24 June. The Hacker News front page this evening did not carry it. US trends at 22:36 UTC were an election slate and Monday Night Football. x.com news returned 403.
Medium A read-only promise on the MySQL and MariaDB connectors of a database MCP server. Medium because the scored vector is CVSS 4.0 6.1. The repository copy says high and stores no vector. Do not average the two.
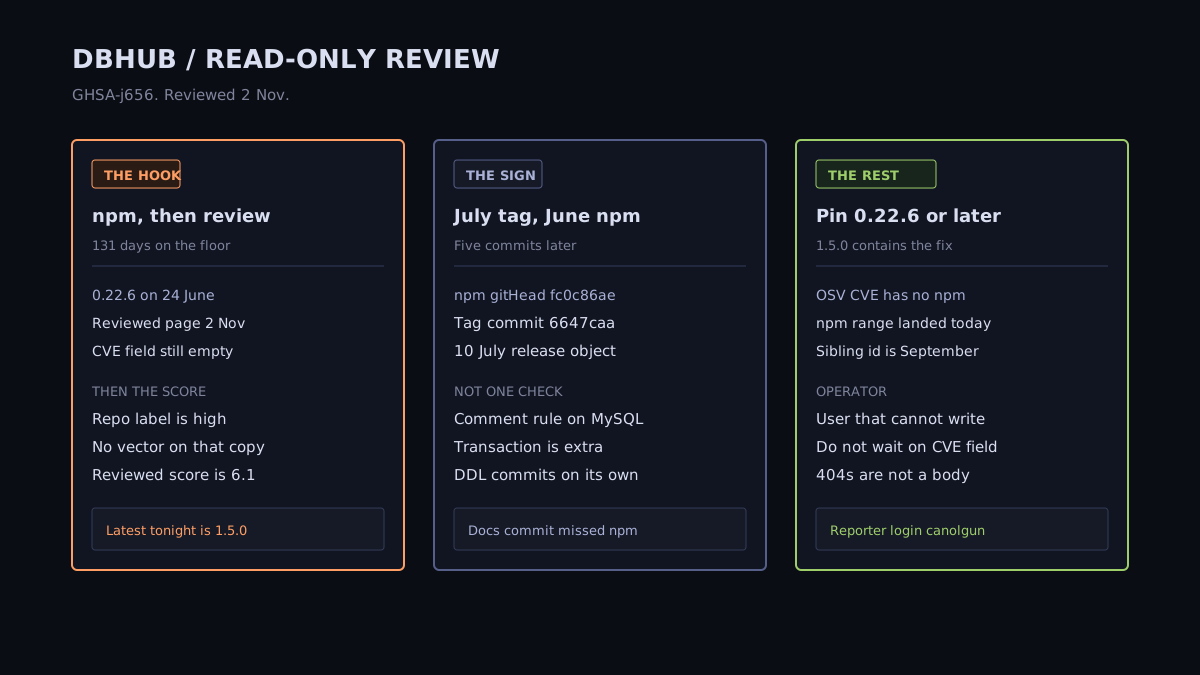
The primary for today's scanner page is the reviewed advisory. published_at 2026-11-02T17:57:51Z. updated_at 2026-11-02T17:57:52Z. github_reviewed_at matches the publish. type is reviewed. cve_id is null. Severity medium. CVSS 4.0 vector CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:P/VC:N/VI:H/VA:H/SC:N/SI:N/SA:N, score 6.1. The CVSS 3.1 vector is null and that score field is 0.0. CWE-436 and CWE-863. Package npm @bytebase/dbhub, range below 0.22.6, first_patched_version 0.22.6. Reporter login canolgun.
The CVE is a different clock. CVE-2026-61789, assigner short name GitHub_M, state PUBLISHED. dateReserved 2026-07-10T20:06:05.616Z. datePublished and dateUpdated 2026-10-30T16:08:24.224Z. datePublic is absent. Reserve to publish is 111d 20h 2m 18.608s. No ADP container. The only metric is the same 4.0 vector. Affected text is below 0.22.6. NVD published 2026-10-30T17:17:26.743Z, 1h 9m 2.519s after the CVE.
The repo advisory's published_at is 2026-06-24T07:42:54Z and its updated_at is 2026-07-10T20:23:36Z. On this read its cve_id is CVE-2026-61789, its severity is high, both CVSS vectors are null, and first_patched_version is null. The range string is below 0.22.6. Do not treat the June published_at as the minute the CVE id appeared. The CVE record itself is 30 October.
| Mark | Clock |
|---|---|
| npm 0.22.5 | 2026-06-24T04:22:32.697Z. gitHead d65c6b42 |
| Commit 872bb338 | 2026-06-24T05:52:24Z. PR 342 merged the same second. Verified |
| Version bump fc0c86ae | 2026-06-24T07:33:52Z. npm 0.22.6 gitHead |
| npm 0.22.6 | 2026-06-24T07:34:34.189Z. 42.189s after the bump |
| Docs commit 6854e839 | 2026-06-24T07:41:48Z. Not in the npm gitHead |
| Repo advisory published | 2026-06-24T07:42:54Z. 8m 19.811s after npm |
| GitHub release v0.22.6 | 2026-07-10T16:49:14Z. Tag 6647caa, committer 16:48:34Z |
| CVE reserved | 2026-07-10T20:06:05.616Z |
| Repo advisory updated | 2026-07-10T20:23:36Z |
| CVE published | 2026-10-30T16:08:24.224Z. 128d 8h 33m 50.035s after npm |
| Reviewed GHSA | 2026-11-02T17:57:51Z. 3d 1h 49m 26.776s after the CVE |
| OSV GHSA modified | 2026-11-02T18:15:06.081593729Z. 17m 15.082s after the review |
From npm 0.22.6 to the reviewed page is 131d 10h 23m 16.811s. npm latest dist-tag is 1.5.0, time 2026-10-09T09:30:54.005Z. GitHub release v1.5.0 published 2026-10-09T09:30:12Z. There is no 1.5.1 key in the times map. modified on the packument is 2026-10-09T09:30:54.353Z.
Compare d65c6b42 to 872bb338 is ahead, ahead 1, behind 0. npm 0.22.5 does not contain the fix. Compare 872bb338 to fc0c86ae is ahead, ahead 1, behind 0. The version-bump commit contains the fix. Compare fc0c86ae to tag 6647caa is ahead, ahead 5, behind 0. The July tag contains the npm commit and is not that commit. Compare 872bb338 to 1.5.0 gitHead 116cfdd2 is ahead, ahead 112, behind 0. This read did not search those 112 commits for a revert.
The July release body includes the pull 342 bullet, "fix: enforce read-only mode at the database engine, not just the keyword classifier." It does not contain CVE or GHSA. It also lists later pulls, including the docs commit and a SQL Server engine change, so it is not a file list of the June npm tarball.
The reviewed summary is a comment-rule mismatch on MySQL and MariaDB. The checker treats two dashes as a comment start no matter what follows. Those engines start that comment only when whitespace, a control character, or the end of the line follows. The advisory says the connectors then run the original string with multiple statements enabled, so a write the checker dropped still reaches the database. This brief does not print a statement.
The 24 June commit message says the classifier was the layer that was wired, and that the change also wraps read-only calls in a transaction. The same message says DDL commits on its own, so the transaction is not the whole fix. The file list includes sql-parser.ts and the MySQL and MariaDB connectors. It does not include execute-sql.ts, which the advisory names as the check. This read did not open the files.
OSV's CVE object was published at the CVE's own timestamp and modified 2026-11-01T02:47:27.036694615Z. It has no package field. The only range is GIT on github.com/bytebase/dbhub, introduced 0, with fixed events at 6647caa and at 872bb338. The extracted notes map those to tag v0.22.6 and to the fix commit. They are not an npm range.
The OSV object id GHSA-j656-3hf2-fvjc was published at 2026-11-02T17:57:51Z. Its package is npm @bytebase/dbhub, introduced 0, fixed 0.22.6. From the reviewed publish to that object's modified time is 17m 15.082s. A scanner that resolved the CVE id through OSV yesterday did not get an npm version floor from that object. A scanner that reads the reviewed GHSA today does.
The same June commit message names four GHSA ids. GHSA-mwwr-p57h-56pf has been in the global database since 2026-09-24T19:37:59Z, severity high, cve_id CVE-2026-61788. Its summary is that read-only mode does not prevent database writes. That is a different id from today's review. GHSA-m689-287g-5xpc and GHSA-7rgf-cwgq-c2qc return 404 on the global API and on the repo API. This read did not find a public body for either.
If the installed version is below 0.22.6, move to 0.22.6 or later. npm 0.22.6 contains commit 872bb338. It does not contain the docs commit from 66 seconds before the repo advisory. Latest 1.5.0 contains both. Pin either. Do not wait for the reviewed page to grow a CVE id. The id is CVE-2026-61789, and NVD stamped it on 30 October.
Keep the database user unable to write. Read-only mode is the control that this record says a comment rule could skip. The docs commit subject is engine-level enforcement and least-privilege guidance. This read did not reopen that page. A green read-only flag on 0.22.5 is the June classifier, not the June fix.
Latest dist-tag tonight is 1.5.0, published 9 October. Compare says that gitHead contains commit 872bb338. The reviewed range is everything below 0.22.6. 1.5.0 is above that floor. This read did not search the commits in between for a revert.
The repo advisory severity field is high, and both CVSS vectors on that object are null. The reviewed database says medium. Its CVSS 4.0 vector scores 6.1, and its CVSS 3.1 vector is null with a score field of 0.0. The CVE record carries the same 4.0 vector and no 3.1 vector. Use the scored vector.
The OSV CVE object was published 30 October and modified 1 November. It has no package field. The only range is a git repo. The OSV object whose id is the GHSA, with the npm semver range fixed at 0.22.6, was published at 17:57 UTC today and modified 17 minutes later.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.