v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
GitBook says an attacker reached infrastructure credentials at 19:00 CET on 2 November. The status update at 12:15 UTC on 3 November told customers to do nothing yet. A later page, stamped 16:21 CET, says personal API tokens were revoked and tells customers to rotate third-party secrets and re-authenticate MCP. The support email's data list does not match that page.
GitBook says an attacker gained unauthorized access to some infrastructure credentials at 19:00 CET on 2 November. The customer rotate list is not on that minute. It is on a page stamped 16:21 CET on 3 November. Hacker News item 50354336, "Gitbook Breached," was created at 2026-11-03T16:45:49Z and was on the front page. US trends at 22:42 UTC were an election slate and Manchester United. The X news tab returned HTTP 200 and a shell titled "X - The Everything App / X," with no news list in the HTML.
High High because the page says every customer's API tokens were invalidated, and because four categories of secrets and questions may have been accessed. There is no CVSS on this incident. There is no customer count.
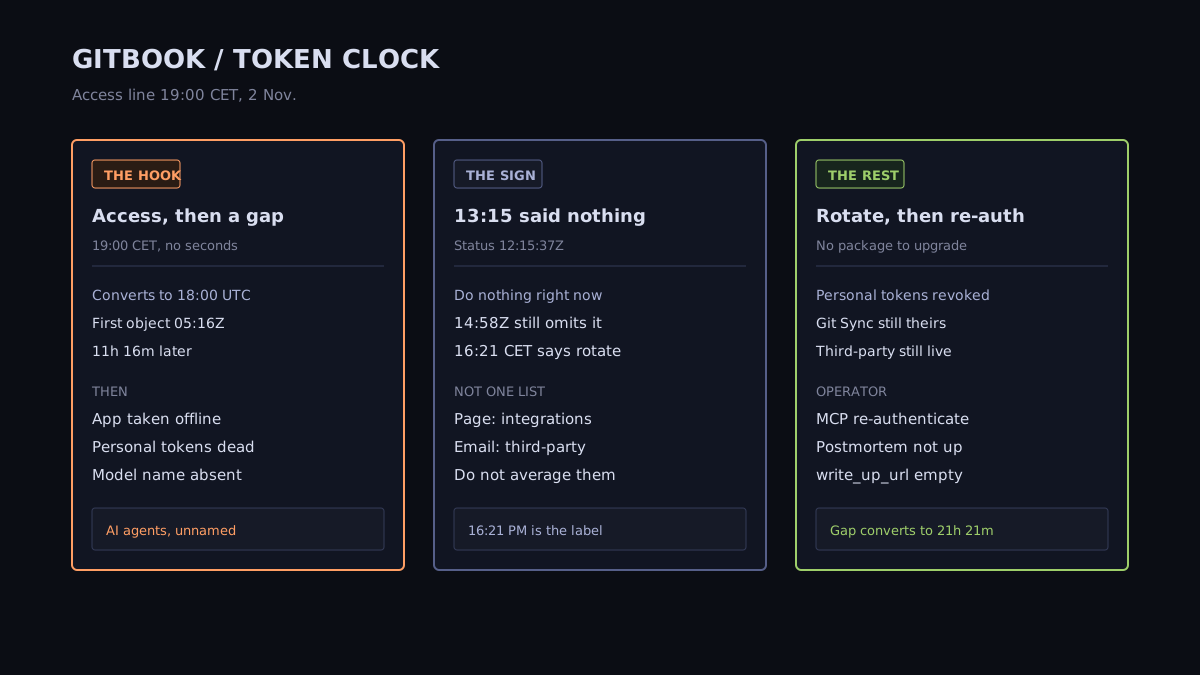
The primary is GitBook's incident page. The visible stamp on the later note is "Tue, Nov 3, 2026, 16:21 CET". A component name on that same node says "16:21 PM". Do not add twelve hours. 16:21 CET is 15:21 UTC, and the line has no seconds. CET on 2 and 3 November 2026 is UTC+1. The access line "19:00 CET, November 2" converts to 18:00 UTC. That conversion is the printed minute, not a measured second.
The page says the attacker used AI agents. It does not name a model, a harness, a CVE, or a package. It says detection was immediate, the app and authenticated docs sites were taken offline, and publicly published content stayed up on cached data. It says GitBook blocked the attacker, closed the vulnerabilities involved, replaced every credential and secret across its infrastructure, and invalidated every customer's API tokens. It does not say when each of those steps finished.
The status incident is a different clock. Name: "Security incident impacting published sites and GitBook app." Four updates, all with published_at:
| Mark | Clock |
|---|---|
| Access line, marketing page | 19:00 CET, 2 November. Converts to 18:00 UTC. No seconds |
| Investigating | 2026-11-03T05:16:51.094Z. Downtime on published sites and the editor. 11h 16m 51.094s after 18:00 UTC |
| Full outage window | GitBook App and Public Content, start 2026-11-03T05:16:51.094Z, end 2026-11-03T12:32:21.423Z. 7h 15m 30.329s |
| Monitoring, no action yet | 2026-11-03T12:15:37.273Z |
| Monitoring, services online | 2026-11-03T12:32:21.423Z. 16m 44.150s later |
| Monitoring, still degraded | 2026-11-03T14:58:12.662Z |
| Rotate note, marketing page | 16:21 CET, 3 November. Converts to 15:21 UTC. No seconds |
| Hacker News item | 2026-11-03T16:45:49Z. 137 points on this read |
From the converted access minute to the converted rotate minute is 21h 21m. Both ends lack seconds, so that gap is not a measured second. The status object's write_up_url is undefined. The marketing page says a full postmortem will be published soon.
The Atom feed also has a resolved entry titled "Git Sync causing missing page content," published 2026-11-02T19:09:51.616Z. Its body says a build change was rolled back. It does not say unauthorized access. A second resolved entry, "GitBook services unavailable," is stamped 2026-11-03T04:52:00.000Z and says monitoring continues on the security incident. The .000Z is the feed's stamp. Do not fold either title into the token list.
The marketing page prints the earlier note as "Tue, Nov 3, 2026, 13:15 cet". A component name on that node says "13:15 PM". 13:15 CET converts to 12:15 UTC. The status update at 2026-11-03T12:15:37.273Z uses the same instruction: investigation still in progress, no confirmation yet of whether customer data was affected, you do not need to do anything right now, steps will be shared after services are restored. This read did not find a field that says the marketing line was generated from that published_at. The prose matches. The marketing line has no seconds.
That update also says unauthorized access to parts of GitBook's infrastructure, contained quickly, some services taken offline. It does not say AI agents. The AI-agent sentence is on the 16:21 CET page.
The 12:32:21.423Z update says both the GitBook App and public content should be online, and that monitoring continues. The 14:58:12.662Z update says some specific issues still affect some customers' published sites, a few services may still be degraded, and monitoring continues. Incident status on that read is Monitoring. The homepage banner said the incident had been ongoing for 17 hours. That duration is a render, not a start minute.
The 16:21 CET page says the attacker may have accessed integrations tokens, Git Sync secrets, API tokens, and questions asked to GitBook Assistant by site visitors. It says there is no evidence that content in GitBook was modified. The action block says rotate any existing GitBook API tokens, and that all personal API tokens were revoked during the incident. It says rotate third-party API tokens or secrets used to connect other tools, rotate secrets in published integrations, and re-authenticate the GitBook MCP server.
The Hacker News item is a support-email paste. The poster wrote that they had not yet seen an official customer communication. The paste's data block says Git Sync secrets, GitBook API tokens, third-party API tokens used to connect external tools, and the same Assistant questions. It does not say "Integrations tokens." Its action block matches the page: personal API tokens revoked, third-party rotation, published-integration secrets, MCP re-authentication. Quote the list on the page you opened. Do not average them into one inventory.
Google News in the two-day window carried a Decrypt item on this incident. That feed pubDate is Tue, 03 Nov 2026 19:46:03 GMT. This brief does not use the rewrite.
The package clock is empty. There is no release to upgrade. The impact clock is the token that GitBook cannot revoke: a third-party secret, a Git Sync secret, and an MCP session that still presents the old credential.
Not in the four updates on the incident object. The 12:15 UTC update says you do not need to do anything right now. The 14:58 UTC update is still about degraded published sites. The rotate list and the MCP line are on the marketing page stamped 16:21 CET, and in a support email pasted on Hacker News.
The page separates them. It says personal API tokens were revoked during the incident, and it also says the attacker may have accessed Git Sync secrets and third-party tokens. Those last two are rotated at the system that issued them. A GitBook-side revoke does not do that work.
The marketing page lists integrations tokens, Git Sync secrets, API tokens, and questions asked to GitBook Assistant. The support email pasted on Hacker News lists Git Sync secrets, GitBook API tokens, third-party API tokens, and the same Assistant questions. Quote the page you opened. Neither list names a model or a customer count.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.
Reviewed GHSA-j656-3hf2-fvjc went up at 17:57 UTC on 2 November with an empty CVE field. npm 0.22.6 has been the fixed build since 24 June.