v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
CVE-2026-117574 published at 20:02 UTC on 28 October. Bugzilla 2494861 is still NEW. The 3 July commit changed lookup, and the score note says that was not a fix.
CVE-2026-117574 published at 20:02:14 UTC on 28 October 2026. An authenticated OpenShift AI gateway caller can name another tenant's model and receive that tenant's provider API key. Bugzilla 2494861 remains NEW. Commit bac9fb5 on 3 July moved lookup off the URL path. The score note says that change was not a fix. The CVE lists no version.
US trends at 22:30 UTC on 28 October were Fofana, Ernie, and Liverpool. Gemini 4 Carbon sat on the same list as a launch. Hacker News led with a fingerprinting note and that launch. X's news tab returned 403. CVE-2026-117574 published at 2026-10-28T20:02:14.895Z.
Critical Critical on the CVSS 3.1 vector, score 9.1, CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:L/A:L. Red Hat's classification word is Important. Bugzilla 2494861 says severity high. The flaw is CWE-639. An authenticated caller can draw another tenant's provider API key.
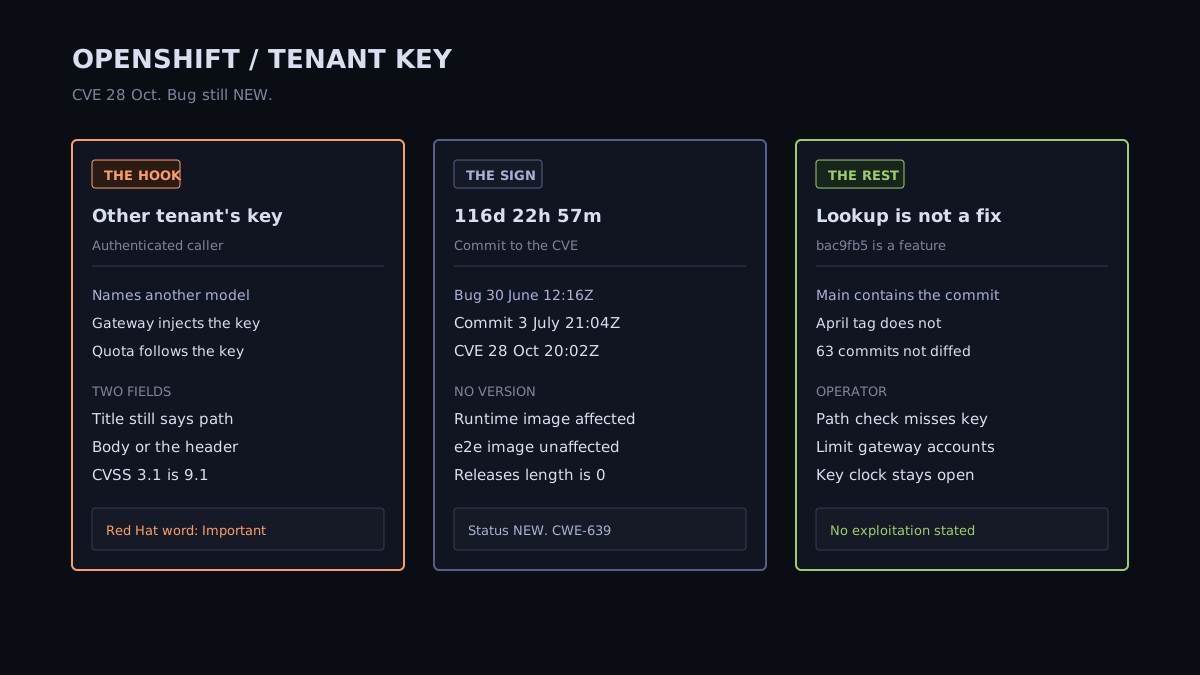
The primary is Red Hat, product Red Hat OpenShift AI, component ai-gateway-payload-processing. The CVE description says an authenticated remote attacker names another tenant's model identifier in the request body or header. The service retrieves credentials from the shared store before it checks authorization, and it injects the target tenant's API key into the request. The caller can then use that tenant's model quota. The statement says the rating is Important because the caller must already hold a valid user credential for the model-serving gateway, which limits unauthenticated use. This brief does not include a request.
The title and the Bugzilla summary still say tenant and credential selection from a client-controlled URL path, with no in-process authorization. The description does not say path. It says body or header. The score explanation, dated 2026-10-27 with no minute, says the score was re-evaluated after the vulnerable mechanism changed and was not fixed. It says the path-based lookup was removed in commit bac9fb5, and credential selection now follows the client-supplied body model field and the x-gateway-model-name header, through a cluster-wide model-name map, still with no in-process identity check. It says subscription validation derives the model identity from the URL path, while credential injection uses the body and the header. Attack complexity moved from high to low on that reading. AV:N is the in-cluster ext_proc gRPC port. There is no CISA ADP record. datePublic is null.
Commit bac9fb55e7e6c9b184720a581054b1ffdc3f62c6 is pull request 359, merged at 2026-07-03T21:04:40Z. The author is Noy Itzikowitz, login noyitz, and the committer time is the same second. The subject is a feature: resolve ExternalModel by body model name for single-URL routing. The message says the resolver prefers the X-Gateway-Model-Name header and falls back to the body model field. Header names are case-insensitive, so that spelling and the score note's lowercase form are one header. Compare of main to this commit is behind, ahead 0, behind 63, so main contains it. This read did not diff those 63 commits for an identity check.
The repository was created 2026-03-12T13:36:58Z. pushed_at on this read is 2026-10-28T18:19:46Z, which is 1 hour, 42 minutes, 28.895 seconds before the CVE. The tip subject is a gRPC size change, commit bb1fee4547, committer 2026-10-28T18:19:45Z. The fifteen newest subjects do not name CVE-2026-117574. Releases length is 0. The only tag is v0.1.0-rc.1, commit 1080e4a56af9cbf78184723586c983177accc335, committer 2026-04-21T12:54:33Z, subject an API translation plugin. Compare of that tag to bac9fb5 is ahead, behind 0, ahead 124. The tag is an ancestor. It does not contain the July commit.
Bugzilla 2494861 is product Security Response, component vulnerability, alias CVE-2026-117574. creation_time is 2026-06-30T12:16:08Z. status is NEW. resolution is empty. is_open is true. cf_last_closed is null. Severity high, priority high. last_change_time is 2026-10-27T12:46:29Z. The score note's 27 October date has no minute, so this brief does not treat that bug timestamp as the score edit.
From the bug open to the July commit is 3 days, 8 hours, 48 minutes, 32 seconds. From the commit to the CVE is 116 days, 22 hours, 57 minutes, 34.895 seconds. From the bug open to the CVE is 120 days, 7 hours, 46 minutes, 6.895 seconds. The CVE dateReserved is 2026-10-27T11:34:15.315Z. From that reserve to datePublished is 1 day, 8 hours, 27 minutes, 59.580 seconds. From the bug's last change to the CVE is 1 day, 7 hours, 15 minutes, 45.895 seconds.
The affected block names two container packages and no versions. rhoai/odh-ai-gateway-payload-processing-rhel9 has defaultStatus affected. rhoai/odh-ai-gateway-payload-processing-e2e-rhel9 has defaultStatus unaffected. Both carry cpe:/a:redhat:openshift_ai. A scanner that stops on the e2e row is reading the test image.
cf_last_closed is null. The fifteen newest commit subjects do not name the CVE. This read did not diff the 63 commits after bac9fb5.X-Gateway-Model-Name. A gateway policy that only binds the path does not cover the field that selects the key.rhoai/odh-ai-gateway-payload-processing-rhel9. The e2e package is unaffected. Neither row has a version. v0.1.0-rc.1 is not a fix line. It predates the commit.The score note says no. It says the path-based lookup was removed in that commit and credential selection moved to the client-supplied model field, with no in-process identity check. The commit subject is a feature for single-URL routing. Bugzilla 2494861 is still NEW, with an empty resolution.
rhoai/odh-ai-gateway-payload-processing-rhel9 has defaultStatus affected. rhoai/odh-ai-gateway-payload-processing-e2e-rhel9 has defaultStatus unaffected. Neither row carries a version. The only Git tag on the upstream repo is v0.1.0-rc.1 from 21 April, and that tag does not contain bac9fb5.
The title still says a client-controlled URL path. The description says another tenant's model identifier in the request body or header. The score note says subscription validation reads the path, and credential injection reads the body and the header. A control that only watches the path does not cover the field the description names.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.