v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
CVE-2026-112346 says pre-1.52.0 OpenHands sandboxes listen on every interface with an empty key list. The 5 October note says loopback. Apptainer hash is unchanged.
VulnCheck published CVE-2026-112346 at 15:34:30 UTC on 26 October 2026. It says OpenHands builds before 1.52.0 bind the sandbox server to every interface with an empty session-key list. GitHub release v1.52.0 went out at 04:10:05 UTC on 5 October. The note says loopback. The empty-list default remains on v1.58.2. The Apptainer file hash is unchanged.
US trends at 22:16 UTC on 27 October were the Colts, Buckner, and Fleetwood. Genie 4 and GPT-6.1 Terra sat on the same day's list as launches. Hacker News led with Genie 4, Ghostty, and a Tailscale SSH note. X's news tab returned 403. CVE-2026-112346 published at 2026-10-26T15:34:30.749Z. Hacker News has no story for the id.
Critical Critical because the record scores 9.3 on CVSS 4.0 and 9.8 on CVSS 3.1, and it says a reachable sandbox port accepts unauthenticated requests. The package change that shipped on 5 October is a Docker host address. The empty session-key list is still the server's own description.
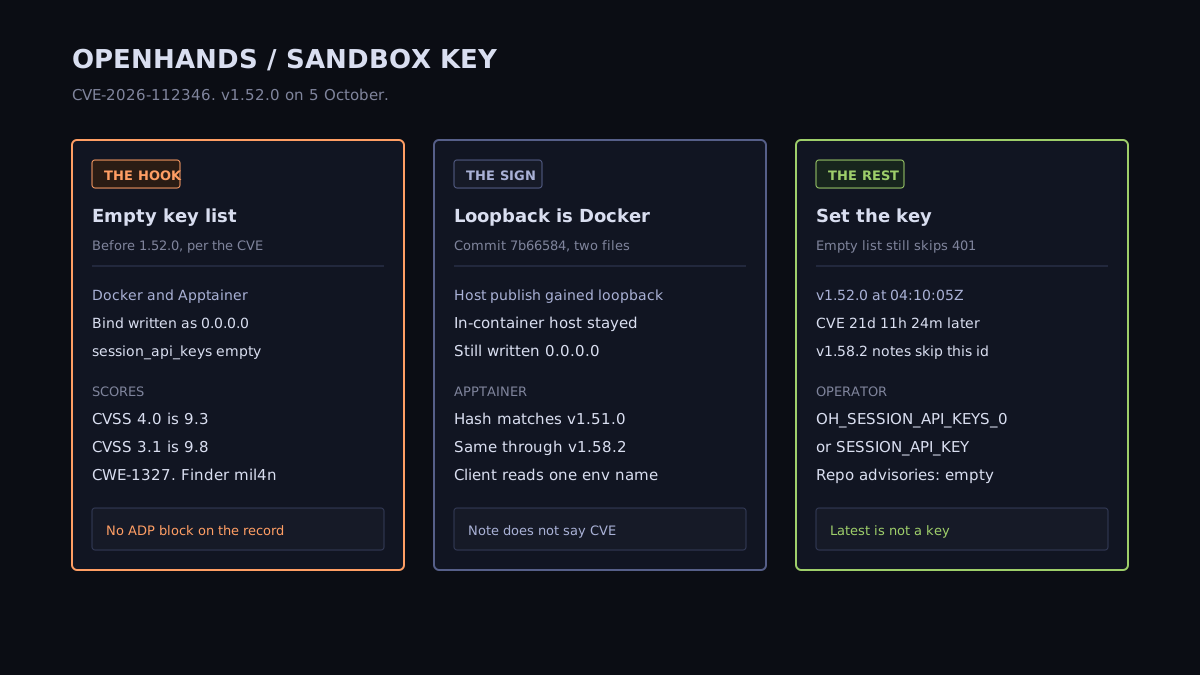
The primary is the VulnCheck CVE record. Assigner short name VulnCheck. State PUBLISHED. dateReserved is 2026-10-19T14:41:46.702Z. datePublished and dateUpdated are both 2026-10-26T15:34:30.749Z. From reserve to publish is 7 days, 0 hours, 52 minutes, and 44.047 seconds. datePublic is 2026-09-21T00:00:00.000Z. From that field to publish is 35 days, 15 hours, 34 minutes, and 30.749 seconds. The weakness is CWE-1327, binding to an unrestricted IP address. CVSS 4.0 is 9.3, CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N. CVSS 3.1 is 9.8, CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H. The finder credit is mil4n. The containers list has no ADP block. The repository security-advisory list is empty.
The affected range is version 0, less than 1.52.0, pkg:github/OpenHands/software-agent-sdk. The description says DockerWorkspace and Apptainer workspace launchers bind the sandbox agent server to all network interfaces, written as 0.0.0.0, with an empty session_api_keys list, which disables authentication by default. It says a caller who can reach the published container port can send unauthenticated HTTP and WebSocket requests, run shell commands as root in the sandbox, reach the mounted workspace, and read plaintext secrets from the secrets store. This brief did not send those requests.
The references are the v1.52.0 release, pull 5209, commit 7b66584ff8899144eb4ce679c2811861342af9de, and the VulnCheck advisory page. Pull 5209 opened at 2026-09-21T16:16:24Z, the same calendar day as datePublic, 16 hours 16 minutes 24 seconds after midnight. Author Graham Neubig. It merged at 2026-10-03T22:42:41Z. From open to merge is 12 days, 6 hours, 26 minutes, and 17 seconds. The merge commit is 7b66584. The commit touches two files: openhands-workspace/openhands/workspace/docker/workspace.py (+11, -3) and tests/workspace/test_docker_workspace.py (+77, -0). No Apptainer path is in that commit. Compare of tag v1.52.0 against 7b66584 is behind, ahead 0, behind 11. Compare of tag v1.58.2 against the same commit is behind, ahead 0, behind 229. The commit is in both tags.
Issue 5379, which the pull says it fixes, opened at 2026-09-29T17:07:06Z and closed at 2026-10-03T22:42:42Z, one second after the merge. The issue is 8 days, 0 hours, 50 minutes, and 42 seconds after the pull opened. The issue body says an agent created it on Neubig's behalf. Do not read 29 September as the day the patch started.
Release v1.52.0 published at 2026-10-05T04:10:05Z. From the merge to that object is 1 day, 5 hours, 27 minutes, and 24 seconds. The note's relevant bullet is "fix(workspace): publish Docker ports on loopback." The note does not say security, authentication, session key, Apptainer, or a CVE. From that release object to the CVE publish is 21 days, 11 hours, 24 minutes, and 25.749 seconds.
PyPI publishes four distributions at the same version. This brief did not download the files. First wheels, none yanked: openhands-agent-server 2026-10-05T04:10:24.400967Z, openhands-sdk 2026-10-05T04:10:25.929500Z, openhands-tools 2026-10-05T04:10:27.370291Z, openhands-workspace 2026-10-05T04:10:28.477265Z. The workspace sdist is 2026-10-05T04:10:32.005190Z. The Docker file the commit edits lives in the workspace package. latest on all four is 1.58.2. The GitHub release v1.58.2 published at 2026-10-25T03:24:42Z. The openhands-workspace 1.58.2 wheel is 2026-10-25T03:25:03.080578Z.
On tags v1.52.0 and v1.58.2, session_api_keys still uses a default factory, and the field text still says an empty list means the server will be unsecured. The request check raises 401 only when that list is non-empty and the presented key is not in it. An empty list skips the 401. That predicate is the same on v1.51.0, which is inside the CVE range, and on v1.52.0, which is the version the CVE calls fixed. v1.58.2 adds a validator that drops a blank string from the list, so an empty value is not itself a credential. The list is still allowed to be empty, and the unsecured sentence is still in the field text.
The Docker host publish string on v1.51.0 is the host port alone. On v1.52.0 and v1.58.2 it is loopback, then the host port, for the agent port and the optional editor port. The in-container server argument in that same file is still 0.0.0.0 on all three tags. The pull says the server keeps listening on the container interface so Docker forwarding still works. The CVE's "all network interfaces" sentence and the release's "loopback" sentence are different sockets. A sandbox whose port is published on a reachable address, on purpose, is outside what the new default publish covers.
The Docker client on v1.51.0 sets its API key to null. On v1.52.0 and v1.58.2 it reads OH_SESSION_API_KEYS_0, then SESSION_API_KEY. If both are unset, the value is still null. The forwarded environment names on the Docker workspace include those two variables. Setting one is what fills the list. The upgrade does not invent a key.
The Apptainer workspace file hashes to 632dba938166a0d1cff5adddae7d35aa9e210e6d75f15ceafb5b910883c77287 on v1.51.0, v1.52.0, and v1.58.2. The server host argument in that file is 0.0.0.0, and the client API key is read from SESSION_API_KEY only. The CVE names this launcher. The patch commit does not. v1.58.2's security bullets are an emSign distrust pin, a Zod lock to 4.6.7, and a Node.js build for CVE-2026-111497. None of them is CVE-2026-112346.
OH_SESSION_API_KEYS_0 or SESSION_API_KEY is what the Docker client reads from v1.52.0 on. If both are unset, the client value stays null, and the server text says an empty list is unsecured. Confirm a request without a key is rejected. This brief did not send one.workspace.py is still 0.0.0.0 on v1.58.2. A port you publish onto a reachable network is not covered by the loopback default. Put a key in front of that port, and keep the sandbox off a shared interface.SESSION_API_KEY only. The CVE names both launchers. The commit names one.The release note does not say that. It says Docker ports publish on loopback. The server field on v1.52.0 and on v1.58.2 still says an empty session-key list leaves the server unsecured, and the request check returns without a 401 when the list is empty. Set OH_SESSION_API_KEYS_0 or SESSION_API_KEY in the environment that launches the workspace. An upgrade that leaves both unset keeps the empty list.
The CVE names DockerWorkspace and Apptainer. Commit 7b66584 changes the Docker workspace file and a Docker test. The Apptainer workspace file is byte-identical on tags v1.51.0, v1.52.0, and v1.58.2. Its server host argument is still 0.0.0.0. Treat the loopback line as the Docker host publish, and read the Apptainer launcher on its own.
It is the latest tag, published at 03:24:42Z on 25 October, and it contains 7b66584. Its notes name an emSign distrust pin, a Zod bump, and a Node.js build for CVE-2026-111497. They do not name CVE-2026-112346. There is no GitHub advisory on the repository. The CVE record has no ADP block.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.