v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GHSA-w4fh-qvv9-3v23 published at 16:00 UTC on 5 October. CVE-2026-116684 followed on 27 October. PyPI mcp 2.3.0 still leaves the audience check unset.
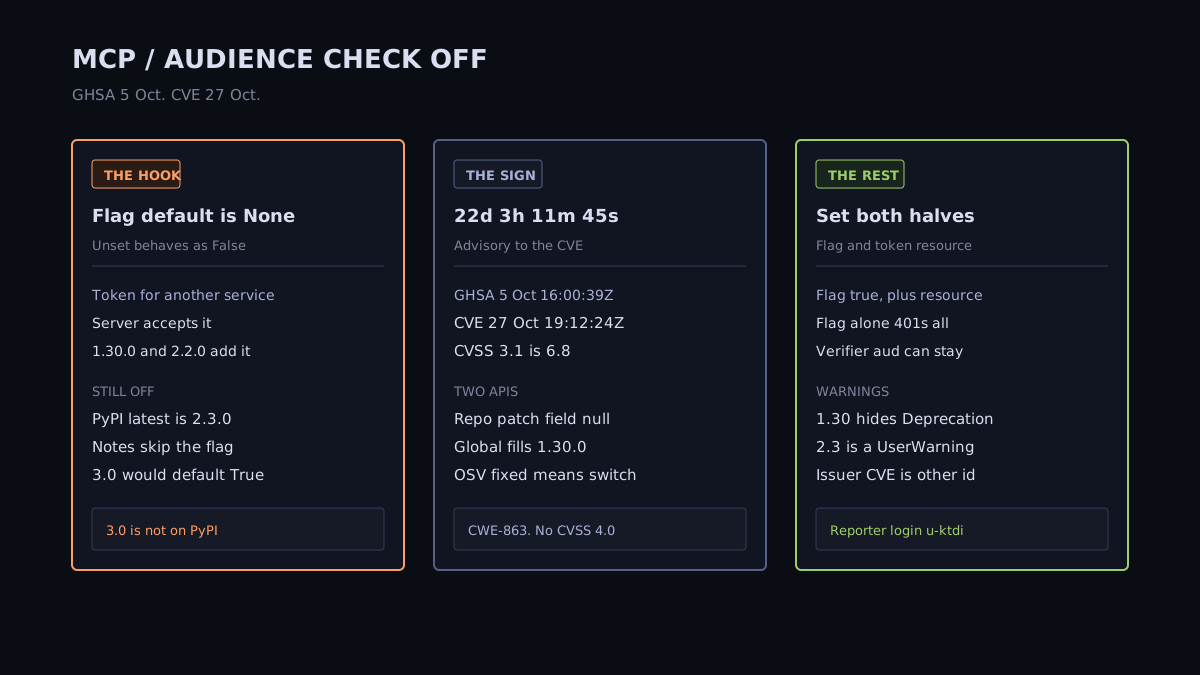
GHSA-w4fh-qvv9-3v23 is the primary. It published at 16:00:39 UTC on 5 October 2026 and says an MCP Python server can accept a bearer token issued for a different resource. Versions 1.30.0 and 2.2.0 add validate_token_resource, which stays off until you set it. CVE-2026-116684 published at 19:12:24 UTC on 27 October. PyPI latest 2.3.0 still leaves the field unset.
US trends at 22:30 UTC on 28 October were Fofana, Ernie, and Liverpool. Gemini 4 Carbon and MacBook sat on the same list as a launch and a laptop. Hacker News led with a fingerprinting note, Gemini 4 Carbon, and an Apple certificate item. X's news tab returned 403. GHSA-w4fh-qvv9-3v23 published at 2026-10-05T16:00:39Z.
Medium Medium because the advisory scores CVSS 3.1 at 6.8, CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:N. CVSS 4.0 is null. The weakness is CWE-863. A token issued for another service is accepted when the server never compares the audience.
The primary is the official MCP Python SDK, pip package mcp. The summary says server-side bearer authentication had no way to check that a token was issued for this server. Where one authorization server issues tokens for several services, a valid token for another service was also accepted. The affected set is an HTTP server using auth=AuthSettings(...) with token_verifier=, an authorization server that also issues tokens for other services, and a TokenVerifier that does not check aud itself. The stated ranges are mcp 1.10.0 through 1.29.1, and 2.0.0 through 2.1.1.
The credit is login u-ktdi, type reporter. The profile name field is the same login. Pull request 3447 merged at 2026-09-05T02:35:56Z onto main, author login maxisbey, merge 0c9136841ff092987a20700ff9c2c9789bda2f40. The commit author name is Max and the committer time is 2026-09-05T02:35:55Z. Pull request 3451 merged at 2026-09-05T02:52:14Z onto v1.x, merge 8c2fa6eabacde869d75568e33b9d466b58c2f512, 16 minutes 18 seconds later. Compare of v2.2.0 to 0c913684 is behind, ahead 0. Compare of v2.3.0 to that commit is behind, ahead 0, behind 35. Compare of v2.1.1 to that commit is ahead, behind 0. Compare of v1.30.0 to 8c2fa6ea is identical. Compare of v1.29.1 to that commit is ahead, behind 0.
settings.py on v1.30.0, v2.2.0, and v2.3.0 declares validate_token_resource with default None. The field text says that with resource_server_url set, leaving it unset warns and behaves as False, and that 3.0 makes True the default there. v1.29.1 and v2.1.1 have resource_server_url and do not have the field. The server passes resource_server_url into the bearer backend only when the flag is true. On the 2.x commit that wiring is in src/mcp/server/lowlevel/server.py and src/mcp/server/mcpserver/server.py. On the 1.x commit it is in src/mcp/server/fastmcp/server.py, twice. None and False are both off.
The advisory's own fix is two changes together. Set validate_token_resource=True, with resource_server_url set to the audience the authorization server puts in tokens for this server. Return that audience from verify_token() as AccessToken.resource. A token for another service then gets 401. With only the first change, every request gets 401. A verifier that already checks the audience can set the flag False to silence the warning. On v1.30.0 the warning class is DeprecationWarning, which Python hides by default. On v2.3.0, MCPDeprecationWarning subclasses UserWarning. v2.2.0 raises that same name. This read opened exceptions.py on v2.3.0, not on v2.2.0.
CVE-2026-116684 is state PUBLISHED, assigner GitHub_M. dateReserved is 2026-10-26T20:00:59.829Z. datePublished and dateUpdated are both 2026-10-27T19:12:24.255Z. datePublic is null. From the reserve to the publish is 23 hours, 11 minutes, 24.426 seconds. From the GHSA published_at to the CVE is 22 days, 3 hours, 11 minutes, 45.255 seconds. The repo advisory updated_at is 2026-10-27T19:10:59Z, which is 1 minute 25.255 seconds before the CVE timestamp. This read did not retrieve the pre-update body. There is no CISA ADP record on the CVE.
The repo advisory API returns cve_id CVE-2026-116684 and leaves first_patched_version null on both pip ranges. The global advisory API, api.github.com/advisories/GHSA-w4fh-qvv9-3v23, published at 2026-10-27T21:06:59Z and updated at 2026-10-27T21:07:01Z. That copy fills first_patched_version with 1.30.0 and 2.2.0. From the CVE to the global publish is 1 hour, 54 minutes, 34.745 seconds. OSV for the GHSA id published at the same 21:06:59Z and modified at 2026-10-27T21:15:03.825987077Z, 8 minutes 4.826 seconds later. OSV for the CVE id published at the CVE timestamp and modified at 2026-10-28T02:54:49.951978440Z.
PyPI, none yanked, one wheel and one sdist:
| Version | Wheel | GitHub release published |
|---|---|---|
| 1.30.0 | 2026-09-07T14:34:14.266679Z | 2026-09-07T14:03:59Z |
| 2.2.0 | 2026-09-07T16:06:19.711091Z | 2026-09-07T15:53:57Z |
| 2.3.0 | 2026-10-02T22:06:52.119073Z | 2026-10-02T22:02:27Z |
latest tonight is 2.3.0. From the v1.30.0 GitHub release to its wheel is 30 minutes 15.267 seconds. From the v2.2.0 GitHub release to its wheel is 12 minutes 22.711 seconds. From the 1.30.0 wheel to the GHSA is 28 days, 1 hour, 26 minutes, 24.733 seconds. From pull request 3447's merge to the GHSA is 30 days, 13 hours, 24 minutes, 43 seconds. The v1.30.0 release object created_at is 2026-09-05T02:52:13Z, the same second as the v1 commit, and published_at is 2 days, 11 hours, 11 minutes, 46 seconds later.
The v1.30.0 and v2.2.0 notes file validate_token_resource under behaviour changes, on the same pages as the client issuer check. The v2.3.0 notes do not contain validate_token_resource or the word audience. OSV's 2.x range is introduced 2.0.0, fixed 2.2.0, and the listed versions stop at 2.1.1. 2.3.0 is outside that list. The source default on 2.3.0 is still None.
This is a different record from GHSA-qx49-fqc8-xw99, the client issuer advisory in those same September releases. On this read that advisory's cve_id is CVE-2026-115563 and updated_at is 2026-10-23T15:40:26Z. This brief did not open that CVE JSON. A scanner row for one id does not close the other.
validate_token_resource=True and AccessToken.resource from verify_token(), equal to resource_server_url. The advisory says the flag alone returns 401 for every request. A verifier that already rejects a foreign aud can set the flag False and keep that check. On 1.30.0 the unset warning is a DeprecationWarning. On 2.3.0 the class subclasses UserWarning.cve_id is CVE-2026-115563, updated_at 2026-10-23T15:40:26Z. CVE-2026-116684 does not close it, and installing 2.3.0 does not pass issuer for you either.first_patched_version null. The global API and OSV name 1.30.0 and 2.2.0. Until the flag is on, reject a token whose aud does not include this server inside verify_token(). That is the advisory's line for every version, including builds from before 1.30.0.No. The advisory says upgrading alone changes nothing. validate_token_resource defaults to None. With resource_server_url set, unset warns and behaves as False. Both the flag and AccessToken.resource from verify_token have to be set. The flag alone answers every request with 401. A verifier that already checks aud can set the flag False to silence the warning.
OSV's range event is fixed at 2.2.0, and 2.3.0 is outside the affected version list. That means the opt-in setting is present. It does not mean the setting is on. The repo advisory API leaves first_patched_version null on both ranges. The reviewed global advisory fills 1.30.0 and 2.2.0. Read the flag on the process, not the word fixed.
No. GHSA-qx49-fqc8-xw99 is the client sending its secret to an authorization server the MCP server chooses. This record, GHSA-w4fh-qvv9-3v23, is the server accepting a bearer token issued for a different resource. They share the 7 September releases. On this read the issuer advisory's cve_id is CVE-2026-115563. This brief did not reopen that CVE body.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.