v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
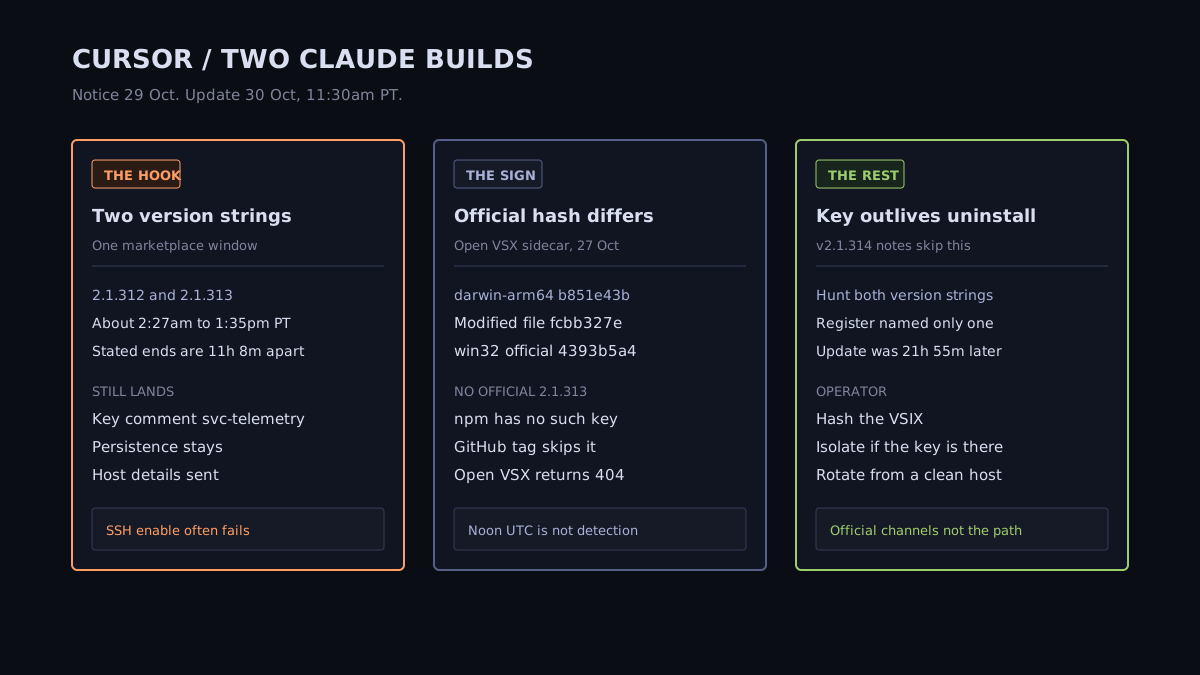
Modified Claude Code 2.1.312 and 2.1.313 sat on Cursor's marketplace for about 11 hours. Open VSX's 2.1.312 hash does not match. Uninstall leaves the key.
Cursor's notice of 29 October says modified Claude Code builds 2.1.312 and 2.1.313 were on its VS Code marketplace from about 2:27am to 1:35pm PT. Anthropic did not publish those copies. Open VSX's darwin-arm64 2.1.312 hash is not the hash Cursor lists for the modified package. npm and GitHub have no 2.1.313. The SSH key and the persistence survive uninstall.
US trends at 22:00 UTC on 30 October were Halloween and Sam Altman. The Hacker News front page was a different clock. Cursor's notice says modified copies of Anthropic.claude-code 2.1.312 and 2.1.313 were on the Cursor VS Code extension marketplace.
The official file and the marketplace file share a version string. They do not share a hash.
High Plugin supply chain on one marketplace. High because the payload drops a key and persistence that survive uninstall, not because a login succeeded on a typical host.
Cursor dates the page 29 October 2026. The structured datePublished and dateModified are both 2026-10-29T12:00:00.000Z, and the visible time element matches. Other posts in the same HTML also use T12:00:00.000Z. Do not treat noon UTC as the minute anyone detected this. The body is the clock.
The body says a maliciously modified Claude Code extension was on the marketplace between about 2:27am PT and 1:35pm PT that day. Those endpoints are 11h 8m apart. Cursor marks both ends as about. Pacific Daylight Time is UTC-7 until 1 November, so the stated window converts to about 09:27 to 20:35 UTC. The packages named are Windows and macOS.
What the extension does, in the notice's own scope: it reports host and user details, appends an attacker-controlled SSH key whose comment is svc-telemetry, tries to enable local SSH and open a reverse tunnel, and tries to keep that tunnel alive with a macOS LaunchAgent or a Windows scheduled task. Cursor says the attacker server no longer functions. It also says that turning SSH on needs admin rights the extension does not have on most macOS and Windows hosts, so that step fails, including outside the unusual case where Cursor itself was started with administrator privileges. The key, the persistence, and the host report still happen. The notice says to follow remediation anyway.
An update line in the body reads 11:30am PT on 30 October: IOCs updated, affected versions clarified. That is 18:30 UTC, 21h 55m after the stated window end. dateModified was still 2026-10-29T12:00:00.000Z on the copy read tonight. The structured date did not move when the version list did.
The Register published at 16:27 UTC on 30 October, 2h 3m before that update line, and still named only 2.1.313. BleepingComputer at 10:36 AM, with no zone on the page, also named only 2.1.313. Hunt both strings. The notice is the list.
The notice does not give a user count. Do not brief one.
The package clock for the official build starts on 27 October, before the marketplace window.
npm @anthropic-ai/claude-code 2.1.312 is 2026-10-27T18:36:10.160Z. GitHub release v2.1.312 is 2026-10-27T20:24:20Z, 1h 48m 9.840s later. Open VSX's darwin-arm64 2.1.312 timestamp is 2026-10-27T20:27:13.052210Z, 2m 53.052210s after that release. The win32-x64 sidecar is 2026-10-27T20:27:56.403203Z.
This read compared Open VSX's published sha256 sidecars with the modified VSIX hashes on Cursor's notice. It did not re-hash the VSIX bytes.
| Platform | Open VSX 2.1.312 sha256 | Cursor modified 2.1.312 sha256 |
|---|---|---|
| darwin-arm64 | b851e43b35b634987ef794fbddc759a7eeabd662088511a276f6063a598373d2 | fcbb327e38e61c4fec795e0d0591f52cd1014b813d20a5912104953c3a17c364 |
| win32-x64 | 4393b5a468057ec65061083604f2db1f03bdd2725f2a72c485eaae6cffe75ddd | 3de1722901165769893bef57c72594e9a54459faa23f3091b136b79966edd081 |
They do not match. A version string of 2.1.312 does not tell you which file you have.
2.1.313 is the version official registries skip. Tonight the npm document has no 2.1.313 key. GitHub matching refs have tags through v2.1.312 and then v2.1.314, and no v2.1.313. Open VSX returns 404 for 2.1.313. Absence is not a deletion log. Cursor says these findings concern the identified package and that it has no evidence other versions or the official distribution are affected.
The modified 2.1.313 hashes exist only on the notice, because there is no official sidecar to compare:
80402fdcad8799285fd93044976973ca000da7995fb93363f819bb8e4f84ee6c6786ec90cbd45949695bd7805c9fbb26cfc91bc5fc897de0183d9bcb9cb21731The notice also gives one payload hash for extension.js in both versions and both of those platforms: ecb58cb29078d9646ad1dcdbe51526f2d9cfea06be5fb2ab183e8ecc3ab6bf15.
From the Open VSX darwin-arm64 timestamp to the stated window start is 1d 12h 59m 46.948s. That gap is the package clock. The impact clock starts when a host loaded the marketplace file, and it does not end when the listing came down.
Cursor says it removed the malicious versions, shut the marketplace, audited access, found no other tampered extensions, rotated its keys, rebuilt the marketplace, and had the attacker server taken offline. Those are Cursor's controls. They do not clear a developer machine.
GitHub v2.1.314 was published 2026-10-30T01:06:26Z, 4h 31m 26s after the stated window end. npm 2.1.314's first timestamp is 2026-10-30T00:12:56.911Z. The v2.1.314 notes do not name the marketplace, Cursor, or 2.1.313. npm's latest tag tonight is 2.1.314. The next tag is 2.1.315 at 2026-10-30T21:05:24.080Z, and GitHub has no release object for v2.1.315. Neither tag is a cleanup step.
The notice's file list also includes Linux paths. The packages it names are Windows and macOS. A Linux path on the IOC list is not, by itself, proof a Linux host downloaded the marketplace build. If the payload ran, the hunt includes the paths the notice lists, including the LaunchAgent label com.apple.sysmond and the Windows task name SysMon.
Separate the two clocks before you close the ticket.
The package clock is the marketplace window, about 11h 8m on 29 October, plus the 27 October official 2.1.312 that must not be confused with it. Search extension-install telemetry for Anthropic.claude-code 2.1.312 and 2.1.313 from the Cursor marketplace in that window. If you still have the VSIX, compare it to the four hashes above. A match to the Open VSX sidecar is the official darwin-arm64 or win32-x64 file. A match to Cursor's hash is the modified one.
The impact clock is whatever the payload already wrote. The public-key fingerprint on the notice is SHA256:0Z6R+DF64Do2nwQic8a7kkfDLNNk4IiK+2U2Rci4htk, comment svc-telemetry. Finding that comment means the host is impacted even if SSH never came up. Isolate that host. Remove the key, the persistence, and any tunnel process using the remediation scripts on the notice, and assume uninstall alone failed. Rotate credentials and sessions that were reachable from the host, from a trusted system. Cursor says the limited environment-variable collection does not rule out later access if the tunnel came up.
Do not turn the notice into a lab. It already contains the check and the cleanup scripts. The operator error is stopping at the version string, or at 2.1.313 only, or at a fresh install.
Cursor's notice says the marketplace builds were not developed by Anthropic, and that it has no evidence other versions or the official distribution were affected. The Register, at 16:27 UTC on 30 October, quotes Felix Rieseberg saying it was not a compromise of Anthropic's systems or employee laptops, that official-channel versions are not affected, and that the impact is Cursor users. Treat that as Anthropic's public position via The Register. This read did not open the post itself.
No. npm published @anthropic-ai/claude-code 2.1.312 at 2026-10-27T18:36:10.160Z. Open VSX's sha256 sidecar for the darwin-arm64 VSIX is b851e43b35b634987ef794fbddc759a7eeabd662088511a276f6063a598373d2. Cursor's modified darwin-arm64 VSIX is fcbb327e38e61c4fec795e0d0591f52cd1014b813d20a5912104953c3a17c364. Match a saved marketplace file to Cursor's hashes, not to the version string.
No. Cursor says uninstalling the extension may not be enough, because the payload drops persistence that keeps running. The v2.1.314 GitHub notes do not name the marketplace, Cursor, or 2.1.313. Isolate a host that shows the key or the persistence, remove those leftovers with the scripts on the notice, and rotate credentials from a trusted system.
Neither string alone. Same-day writeups named only 2.1.313. The notice update at 11:30am PT on 30 October names 2.1.312 and 2.1.313. A host that updated inside Cursor during the window can show 2.1.312 and still be the modified file.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.