v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
A public ChatGPT share ran in the signed-in session. OpenAI closed both frontends on 26 October. MathLive's default stayed none until 20:28 UTC on 31 October.
Parameter's 28 October post says a public ChatGPT share could run code in the signed-in session of whoever opened it. The Preview sandbox held. A graph on the same page loaded MathLive, whose listener accepted a keyboard message from any origin. OpenAI closed both frontends on 26 October. MathLive's documented default stayed none until 20:28:46 UTC on 31 October.
A public ChatGPT share could run inside the signed-in session. Parameter's post, by Mukul Goyal and dated 28 October 2026, says the Preview sandbox held. A graph on the same page loaded MathLive, and that listener did not.
The Hacker News item 50314699 was created at 2026-10-31T10:30:11Z. This front-page read showed 293 points. US trends at 22:16 UTC were Halloween, boxing, and college football. X News did not load on this run.
High Session boundary on a signed-in chat product. High because the proof called the signed-in APIs, including a private conversation that had never been shared. OpenAI's fix date is 26 October. The library default moved on 31 October.
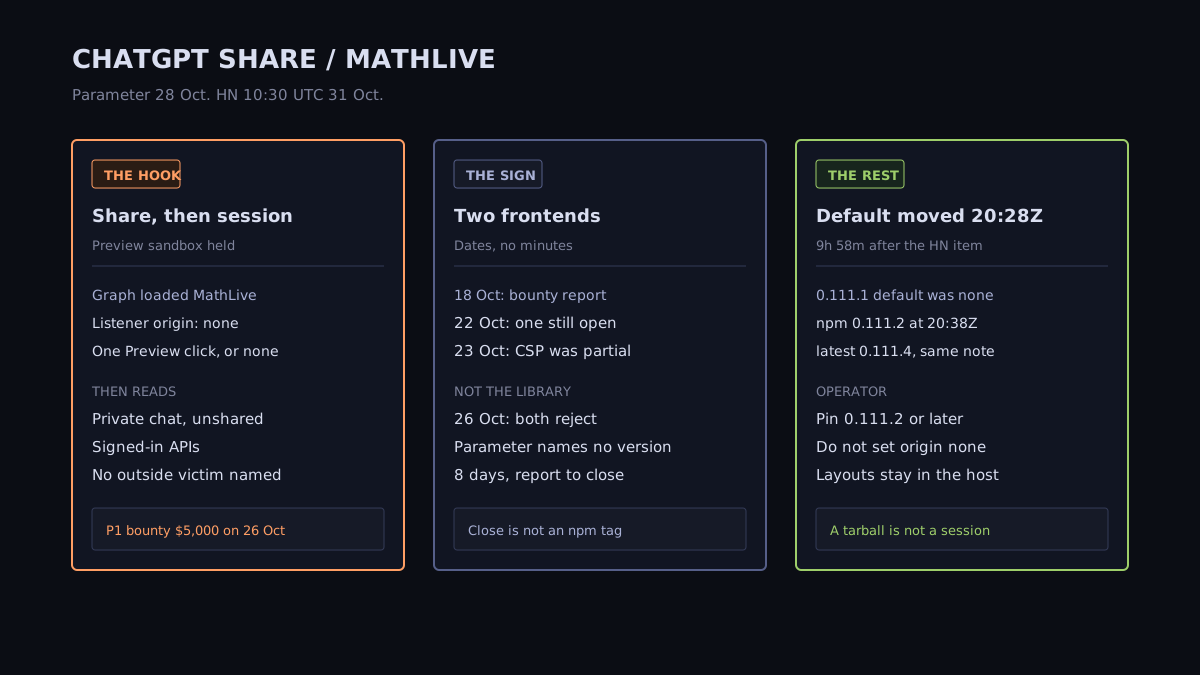
Parameter's timeline has dates and no minutes. Do not invent a clock inside a day.
| Date | What Parameter records |
|---|---|
| 13 October | Message-to-HTML path confirmed against production ChatGPT |
| 14 October | Chain reproduced in the normal UI |
| 16 October | Public share delivered between separate accounts, one Preview click |
| 17 October | Automatic Preview from the share, including after a hard refresh |
| 18 October | Report submitted to OpenAI's bug bounty |
| 19 October | Private-chat proof added |
| 21 October | OpenAI reproduced it. Severity raised from the initial P2 triage to P1 |
| 22 October | One web frontend fixed. The second still updating |
| 23 October | CSP changes blocked part of the chain. One frontend update remained |
| 26 October | Both frontends rejected the reported messages. Resolved. Bounty 5,000 dollars |
| 28 October | The post's byline. No minute |
From the 18 October report to the 26 October resolution is eight calendar days. From the 13 October confirmation to that resolution is thirteen. The Hacker News, by Swati Khandelwal, is dated 31 October and prints no minute. A Google News RSS pubDate for that item is 05:33:00 GMT on 31 October. That is a feed stamp, not a byline minute on the THN page.
The stable proof needed one click on ChatGPT's Preview button. The later version opened Preview on its own. Parameter reproduced that automatic path three times in a separate account, including after a hard refresh, with an alert after roughly 4.5 seconds. Opening the shared link was the only required action in that version. The victim did not install an app, join a project, or sign in through the attacker.
What the code could do, in Parameter's own scope: enumerate the victim's recent conversations, retrieve a private conversation that had never been shared with the attacker, and send a small piece of that response to a server Parameter controlled. Parameter says the code was not limited to that proof. Because it ran as chatgpt.com, other actions exposed to the signed-in web app sat inside the same boundary. The post does not name an outside victim.
The conversation contained an ordinary interactive graph. Loading that graph loaded MathLive into the main page and installed a listener there for the on-screen keyboard. Parameter says the listener's origin policy was none, so it accepted a message from any web address, and that the keyboard-layout field could carry HTML. That HTML could create a frame the browser treated as chatgpt.com. A script host already allowed by ChatGPT's content security policy then supplied the code. Parameter says blocking that host would have removed one path to script and would have left the HTML path in place.
This brief does not repeat the message, the layout field, the script URL, or the conversation API paths. Those are in the post. They are not an operator checklist.
Three decisions, as Parameter lists them: the listener acted on a state-changing message without proving which frame sent it; the message could carry raw HTML as layout data; that HTML could create an unsandboxed document that inherited the chatgpt.com identity.
On 22 October one frontend was fixed and the second was not. On 23 October, CSP changes blocked part of the chain while one frontend update remained. On 26 October both frontends rejected the messages used in the report. A host that only picked up the CSP change, or only one of the two frontends, was not the close Parameter describes.
Parameter does not name the MathLive version ChatGPT loaded. The package clock is the library's own record. The impact clock is the signed-in session, and it does not move when npm does.
npm mathlive 0.111.1 is 2026-10-09T09:58:09.377Z. Its git head is 30ad20a7a47ea43a2f6915808023202c78f37742, committer 2026-10-09T09:52:01Z, 6m 8.377s earlier. The options file on that commit still documents the keyboard default as "none". The 0.111.1 changelog security note is a different bug, in the shadow option of the \enclose command. It is not this listener.
Commit db6e36feb5 is author and committer Arno Gourdol at 2026-10-31T20:28:46Z. The subject is same-origin validation for virtual keyboard messages. The 0.111.2 changelog says four things: the default is now same-origin; cross-window settings can select built-in layouts but cannot supply custom layouts or keycap overrides, even with origin validation disabled; a state-changing message cannot select a new recipient; same-origin checks no longer treat unrelated opaque origins as equal, and they do not accept a wildcard as a sender. MathfieldElement.createHTML remains an integration hook. Its default returns the supplied HTML unchanged.
Tag v0.111.2 is commit b64255b7d067ff3a13fe289b677ae7f92028c5d3 at 2026-10-31T20:34:35Z. Compare against the fix commit is ahead, behind 0, ahead 8. The tag contains the fix. npm 0.111.2's git head is that tag, at 2026-10-31T20:38:48.274Z. Commit to tag is 5m 49s. Tag to npm is 4m 13.274s.
From the Hacker News item at 10:30:11Z to the fix commit is 9h 58m 35s. The library change is five calendar days after the date OpenAI named. There is no minute on 26 October, so this brief does not convert that gap into seconds.
npm latest tonight is 0.111.4 at 2026-10-31T21:10:34.684Z, git head c3f819a501c237a8c04dc5c207162fc04577a30f. 0.111.3 is 2026-10-31T20:40:50.439Z. From 0.111.2 to 0.111.4 is 31m 46.410s. The changelog fetched on the 0.111.4 commit still opens with the 0.111.2 security section. Those later publishes are not a second keyboard fix.
There is no ChatGPT package for a user to patch. The date Parameter gives for both frontends is 26 October. If a signed-in browser opened an untrusted share between the 16 October public-share proof and that fix, treat the private conversations as exposed to that share. Parameter gives no user count. Review account changes you did not make. Do not brief a victim total from a bounty writeup that never counted one.
If you embed MathLive on a page an untrusted frame can reach, move to 0.111.2 or later. Do not set originValidator to none on that page. Put custom HTML layouts in the keyboard's host window. The 0.111.2 notes say a cross-window message cannot supply them, including when origin validation is disabled. createHTML will not sanitize a string you mark as trusted.
Keep the two clocks apart. ChatGPT's impact clock is the signed-in session, closed on the date OpenAI confirmed both frontends. MathLive's package clock closed at 20:28:46Z on 31 October, 9h 58m 35s after the front-page post. A newer tarball does not close the other one.
No. Parameter says both ChatGPT web frontends rejected the reported messages on 26 October. MathLive commit db6e36feb5, which changes the documented default from none to same-origin, is 20:28:46 UTC on 31 October. npm 0.111.2 follows at 20:38:48.274Z. The chatgpt.com fix and the npm tarball are different clocks.
No. The 0.111.1 changelog security note is an enclose-command markup bug. The options file on that version still documents the keyboard default as none. The keyboard notes start under 0.111.2.
Parameter does not name an outside victim. The post says the public-share proof ran between separate accounts, and that OpenAI reproduced the execution and the private-conversation proof. Absence of a victim list is not a measurement of zero use.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.