v0.51.0 Beat the sbx cp CVE by Two Hours.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
Three Beta9 sandbox CVEs landed on 1 November. Worker 0.1.756 and gateway 0.1.776 were tagged on 15 September. The notes do not name the CVEs.
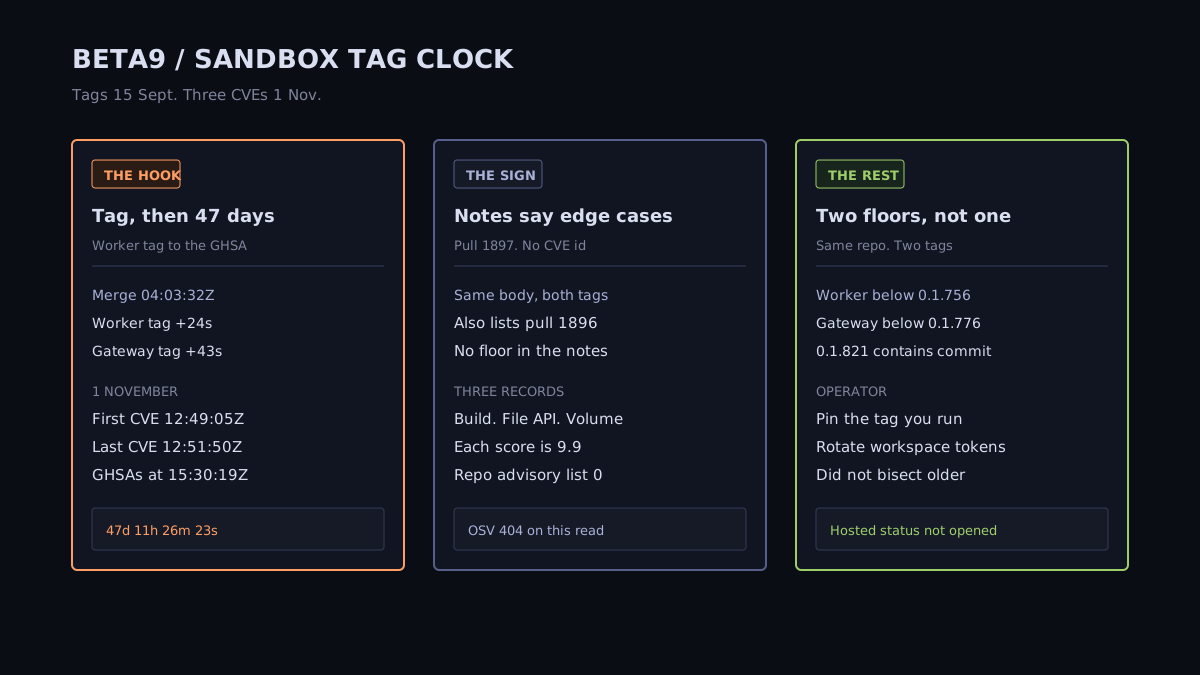
JFrog published three Beta9 sandbox CVEs on 1 November, each CVSS 3.1 9.9. They name one commit, merged on 15 September and tagged worker 0.1.756 twenty-four seconds later. Gateway 0.1.776 followed nineteen seconds after that tag. The notes say sandbox edge cases and do not name the CVEs. GitHub's copies are unreviewed, with an empty package list. OSV returned 404.
JFrog published three Beta9 sandbox records on 1 November. The commit they share was already tagged on 15 September. beam-cloud/beta9 describes itself as serverless GPU inference, sandboxes, and background jobs. The Hacker News front page this evening did not carry the CVEs. US trends at 22:24 UTC were NFL games and election names. x.com news returned 403.
Critical Tenant isolation on the sandbox runtime. Critical because each GitHub advisory is CVSS 3.1 9.9, CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H. The privilege is a workspace token, not an anonymous internet caller. None of the three CVE records has an ADP container, and datePublic is null on each.
The primaries are the three CVE records. Assigner short name JFROG. State PUBLISHED. They name the same pull, 1897, and the same commit, a28bf12cf0007c792a25d8ed282b4e8bf6f30393. This read did not open the patch. The control text below is the records.
Pull 1897 was opened at 2026-09-14T15:26:01Z by luke-lombardi and merged at 2026-09-15T04:03:32Z. Open to merge is 12h 37m 31s. The commit subject is "Handle sandbox edge cases (#1897)." Author date and committer date are that same second. Committer name is GitHub. Verification is valid.
| Tag or id | When it moved |
|---|---|
| worker-0.1.745 | 2026-09-07T02:47:06Z. Compare to the commit: ahead, ahead 18, behind 0 |
| gateway-0.1.769 | 2026-09-07T04:12:51Z. Compare: ahead, ahead 17, behind 0 |
| worker-0.1.756 | 2026-09-15T04:03:56Z. 24s after the merge. Compare: identical |
| gateway-0.1.776 | 2026-09-15T04:04:15Z. 43s after the merge. Compare: identical |
| CVE-2026-120306 | Reserved 12:32:40.057Z. Published 12:49:05.857Z. 16m 25.800s |
| CVE-2026-120307 | Reserved 12:45:12.430Z. Published 12:49:51.981Z. 4m 39.551s |
| CVE-2026-120308 | Reserved 12:46:51.095Z. Published 12:51:50.481Z. 4m 59.386s |
| NVD stamp on the GHSAs | 2026-11-01T13:18:01Z on all three |
| Three GHSAs | 2026-11-01T15:30:19Z |
Those reserve and publish times are 1 November. From the worker tag to the GitHub advisories is 47d 11h 26m 23s. From the gateway tag to the same advisories is 47d 11h 26m 4s. The three CVE publishes sit inside 2m 44.624s of each other, from 12:49:05.857Z to 12:51:50.481Z. The NVD field on each GitHub advisory is the same second, 13:18:01Z. From that stamp to the GHSA publish is 2h 12m 18s.
GHSA-xvhg-75x6-gj86 is CVE-2026-120306, updated at 15:30:30Z. GHSA-6h4h-qffc-3gfp is CVE-2026-120307, updated at 15:30:20Z. GHSA-92w2-g272-fr77 is CVE-2026-120308, updated at 15:30:30Z. The publish second is shared. The update second is not.
CVE-2026-120306 is the build sandbox. The record says image-build steps use chroot isolation, so they keep the worker's namespaces and run as root on a privileged worker pod. The scenario line is a default clip v2 layered image build. The range is worker version 0 lessThan 0.1.756. CWE-269. Fixed text: OCI isolation with private namespaces. Package files named include the worker image build path. This brief did not bisect tags under 0.1.756.
CVE-2026-120307 is the sandbox file API. The record says the worker resolves a tenant path on the worker, outside the container, and that upload, download, stat, list, and delete all use that helper. The scenario line is a workspace token plus one running sandbox. The range is worker version 0 lessThan 0.1.756. CWE-22. The fix text says later file operations use a rooted open. The record also says a read of the worker service-account token succeeded from that API, and that the shipped remote-node manifests bind that account to cluster-admin. This brief did not open those manifests.
CVE-2026-120308 is the volume mount. The record says a workspace token can attach a volume whose identifier is not checked for ownership, and that a bad identifier can mount the worker filesystem into the sandbox. It says this was confirmed against gateway 0.1.769 and worker 0.1.745. The range is gateway version 0 lessThan 0.1.776 and worker version 0 lessThan 0.1.756. CWE-22. The fix text says identifiers, mount paths, and ownership are checked, including for stubs saved earlier. From the confirmed worker tag to worker 0.1.756 is 8d 1h 16m 50s. From the confirmed gateway tag to gateway 0.1.776 is 7d 23h 51m 24s. Those confirmed tags are one pair, not a proof that every older tag behaves the same way.
The package name on all three records is github.com/beam-cloud/beta9. Gateway and worker are different GitHub release tags on that repo, not two PyPI versions of one number. Compare says worker-0.1.745 and gateway-0.1.769 do not contain a28bf12. Compare says worker-0.1.756 and gateway-0.1.776 are that commit.
The newest tags on this read are not those floors. worker-0.1.821 was published at 2026-10-31T13:39:10Z. Compare to the commit is ahead, behind 0, ahead 142. gateway-0.1.840 was published at 2026-10-31T15:08:37Z. Compare is ahead, behind 0, ahead 143. Both contain the commit. From worker 0.1.756 to worker 0.1.821 is 46d 9h 35m 14s. From gateway 0.1.776 to gateway 0.1.840 is 46d 11h 4m 22s. Repo pushed_at is 2026-10-31T20:59:02Z, after both of those tags. This read did not review the commits after 0.1.840.
Each GitHub advisory is type unreviewed. github_reviewed_at is null. vulnerabilities is an empty array. Severity is critical and the score is 9.9. OSV returned 404 for CVE-2026-120306, CVE-2026-120307, CVE-2026-120308, and GHSA-92w2-g272-fr77. The repository security-advisory list length is 0. A scanner that keys off OSV, or off a reviewed package range, does not learn these tags from those endpoints tonight. The floors are in the CVE prose.
If you run the open source worker below 0.1.756, move it. If you run the open source gateway below 0.1.776, move that too. A current checkout of worker 0.1.821 and gateway 0.1.840 already contains a28bf12. Pin the tags you actually deployed. Do not treat "latest" as a substitute for reading which binary is on the node.
The 9.9 score assumes a workspace token. Rotate tokens that could deploy a function, an endpoint, a task queue, or an image build on a node still below the floor. The file-API record's impact is the worker and the other tenants on that machine, and it names cluster-admin on the shipped remote-node manifests. Check that binding on the manifests you run. This read did not open a hosted status page, so a cloud tenant is not cleared by an upstream tag existing.
Read the 15 September notes as a product line. Then read the three CVE titles. Edge cases is the commit subject. It is not the disclosure.
Not from the worker number. CVE-2026-120308 sets the gateway floor below 0.1.776 and the worker floor below 0.1.756. They are separate release tags. This brief did not run a gateway build between 0.1.769 and 0.1.776.
No. Worker 0.1.756 and gateway 0.1.776 both list pull 1897 as handle sandbox edge cases. They do not print CVE-2026-120306, CVE-2026-120307, or CVE-2026-120308. The repository security-advisory list length is 0.
Compare of the fix commit to worker-0.1.821 is ahead, behind 0, ahead 142. Compare to gateway-0.1.840 is ahead, behind 0, ahead 143. Both tags contain the commit. That is the open source tag, not a statement about a hosted control plane.
Docker Sandboxes v0.51.0 published at 14:06 UTC on 3 November. CVE-2026-103916 followed at 16:19. The range still ends before 0.51.0.
GitBook's 13:15 CET note said no customer action. The 16:21 CET page says rotate API tokens and re-authenticate the MCP server.
Amazon published CVE-2026-116635 at 21:34 UTC on 2 November. The 0.2.1 wheel had been on PyPI since 30 October. The release note does not say CVE.